Skip to content

21 August 2026 | 9 min

EU Retail Investment Strategy: Why “Value for Money” Is Becoming the New GRC Benchmark in Financial Distribution

The EU Retail Investment Strategy aims to strengthen the European market for retail investments while improving investor protection. At the centre of the reform is a concept that will become highly relevant for banks, insurers, asset managers, wealth managers and financial distributors: “Value for Money”.

The message is clear: in future, financial institutions will not only need to disclose costs, risks and product characteristics correctly. They will increasingly need to demonstrate that a product provides fair value for its intended target market.

This shifts the regulatory focus. Product documentation becomes product governance. Cost transparency becomes evidence. Distribution control becomes a GRC topic that connects requirements, target markets, costs, client outcomes, remuneration, marketing and audit trails.

The EU Retail Investment Strategy reforms key rules for financial distribution, including areas linked to MiFID II, IDD, PRIIPs, UCITS and AIFMD. Its objective is to improve investor protection, make access to capital markets easier and increase trust in financial products.

The main GRC driver is “Value for Money”. Financial products should not only be transparent. They should provide a demonstrable and reasonable balance between costs, fees, risks, performance potential and client benefit.

For financial institutions, this means stronger requirements for product approvals, target market definitions, cost and fee analysis, suitability processes, inducements, marketing controls and evidence management.

Swiss institutions may also be indirectly affected, particularly through EU subsidiaries, EU branches, cross-border distribution or EU distribution partners.

Why “Value for Money” Marks a Shift

Financial distribution regulation has long focused on transparency. Clients should understand what a product costs, which risks it carries and what characteristics it has. That remains important, but it is no longer enough.

Value for Money goes further. The question is no longer only whether everything has been disclosed. The question is whether the product is appropriate for the target market when costs, services, performance potential, risk and distribution model are considered together.

This is a shift from formal compliance to outcome-oriented governance. A product can be correctly documented and still become problematic if costs and fees are not proportionate to the expected client benefit.

For GRC leaders, this is the key point. Value for Money does not create a single new checklist. It requires existing processes to be connected. Product development, product approval, target market assessment, cost analysis, distribution, advice, marketing and ongoing monitoring must work together.

Product Governance Becomes More Evidence-Based

Financial products are often created and distributed through complex structures. Asset managers, issuers, banks, platforms, insurers and distributors may all have different roles. The Retail Investment Strategy increases the pressure to document these roles more clearly.

Product manufacturers must be able to explain why a product is suitable for the defined target market. This includes a clear assessment of costs and fees. Distributors, in turn, must ensure that they recommend or offer products only to clients for whom they are appropriate.

This makes product governance more operational. Institutions must not only have a product approval process. They must be able to show which criteria were reviewed, which data was used, what trade-offs were considered and who approved the decision.

For compliance and internal audit teams, this is crucial. The audit question will not only be whether a process exists. It will be whether the process leads to appropriate decisions and whether those decisions are documented in a defensible way.

Costs, Fees and Client Benefit Move Closer Together

Value for Money turns costs and fees into a central governance data point. Institutions must not only disclose costs, but place them in the context of client value. Peer group comparisons, benchmarks, cost structures, expected returns, risk-return profiles and target market assumptions may all become relevant.

This is challenging because many data sources are involved. Product data, cost information, performance data, risk metrics, target market information, remuneration structures and distribution data often sit in different systems. If these data points are inconsistent, evidence gaps emerge.

A product may be considered appropriate during product approval, while distribution materials later use outdated cost information. Or a product may be approved for a defined target market but marketed too broadly through digital channels. These inconsistencies are exactly where GRC risks arise.

Inducements Remain a Control Topic

Inducements are one of the most sensitive issues in the Retail Investment Strategy. The political debate around a full ban has been intense. The current direction is more focused on stronger controls, better transparency and evidence that client interests are protected.

For institutions, this means that remuneration models must be connected more closely with product governance and distribution controls. It must be clear which incentives exist, how conflicts of interest are identified and which controls prevent remuneration from improperly influencing product selection or advice.

Inducements are therefore not only a legal or disclosure topic. They become part of the internal control system. Institutions must be able to show that remuneration, product approvals, client interests and advisory obligations are assessed together.

Suitability and Distribution: From Client Profile to Evidence Chain

Suitability processes will also become more important. In investment advice and distribution, institutions must be able to demonstrate that a product fits the client’s knowledge, experience, risk tolerance, investment objectives and ability to bear losses.

The GRC issue lies in the evidence chain. A single advisory form is not enough if the underlying product data, target market definition, cost information and distribution rules are not aligned. Institutions must ensure that recommendations result from a consistent process.

This is particularly relevant for digital distribution channels. Robo-advice, online platforms, app-based investment offerings and automated product recommendations generate large volumes of data and decisions. These need to remain controlled, versioned and auditable.

Marketing Becomes Part of Product Governance

Marketing in financial distribution is not just communication. Product descriptions, performance statements, ESG references, cost information, risk warnings and digital campaigns influence how clients understand a product.

Value for Money strengthens this connection. If a product is promoted with certain benefits, the marketing message must align with product governance, target market definition and the cost-benefit assessment. Marketing claims cannot be created in isolation.

For GRC teams, this creates a clear need for approval and control processes. Product information, campaigns, websites, factsheets and digital distribution materials should be reviewed and versioned in a traceable way. This becomes even more important in cross-border distribution, where requirements and supervisory expectations may differ by market.

Why Swiss Institutions Should Pay Attention

The Retail Investment Strategy is EU regulation. Swiss financial institutions are therefore not automatically directly affected. However, the topic is relevant for many Swiss providers.

This applies especially where an institution has EU subsidiaries, EU branches, EU distribution partners or cross-border business with EU clients. Even if a Swiss institution is not directly addressed, EU partners may request additional evidence.

In practice, this may mean that Swiss asset managers, wealth managers or product providers need to document more clearly how costs, target markets, product benefits, risks and distribution information fit together. EU distribution partners will need this information to meet their own obligations.

This creates an indirect GRC effect across the distribution chain.

What Financial Institutions Should Do Now

Institutions should first assess whether their product governance is ready for Value for Money. This is not only about product approvals. It is about whether costs, target markets, client benefit, risk, remuneration and distribution are assessed and documented consistently.

They should then review which data sources are used for costs, performance, risk, target market and distribution. If this data is not current, consistent or centrally available, implementation risk increases.

A review of distribution channels is also important. Personal advice, digital platforms, insurance distribution, cross-border distribution and partner distribution all create different control points. Value for Money must work across all relevant channels.

Finally, institutions should define the audit trail early. Trying to reconstruct decisions later creates unnecessary effort and risk.

Conclusion: Value for Money Makes Financial Distribution More Auditable

The EU Retail Investment Strategy shows where financial regulation is heading. Transparency remains important, but it is not enough. Products for retail clients should not only be understandable. They should provide demonstrable value.

For GRC leaders, the direction is clear: product governance is becoming more outcome-oriented and more evidence-based. Institutions need to connect costs, target markets, client benefit, remuneration, distribution and controls more closely.

Those that build structured processes, clear responsibilities and audit-ready evidence early will reduce regulatory risk and strengthen trust with clients, supervisors and distribution partners.

Zazoon supports financial institutions in managing Value for Money as an integrated GRC process: from requirements and product governance to risks, controls, evidence, findings and management reporting.

FAQ

What is the EU Retail Investment Strategy?

The EU Retail Investment Strategy is a reform package designed to strengthen the retail investment market in Europe. It aims to improve investor protection, enhance product information and make access to capital markets easier.

What does “Value for Money” mean?

Value for Money means that financial products should provide appropriate value for the intended target market. Costs, fees, risks, services and client benefit must be aligned in a demonstrable way.

Which financial institutions are affected?

The topic is particularly relevant for banks, investment firms, asset managers, insurers, insurance distributors and other financial service providers with EU exposure.

Why is Value for Money a GRC topic?

Because it connects product governance, cost analysis, target market definition, suitability, inducements, marketing controls and evidence. It is not only about disclosure, but about auditable decision-making.

Are Swiss institutions affected?

Not automatically. However, Swiss institutions may be indirectly affected if they have EU subsidiaries, EU branches, EU distribution partners or cross-border business with EU relevance.

What should institutions do now?

They should review their product governance, cost and fee processes, target market definitions, distribution controls, inducement controls and audit trails for Value for Money readiness.

How does Zazoon help?

Zazoon helps connect requirements, products, target markets, risks, controls, approvals, actions and evidence in one central GRC system. This makes Value for Money traceable, manageable and audit-ready.

Related posts

18 August 2026 | 9 min

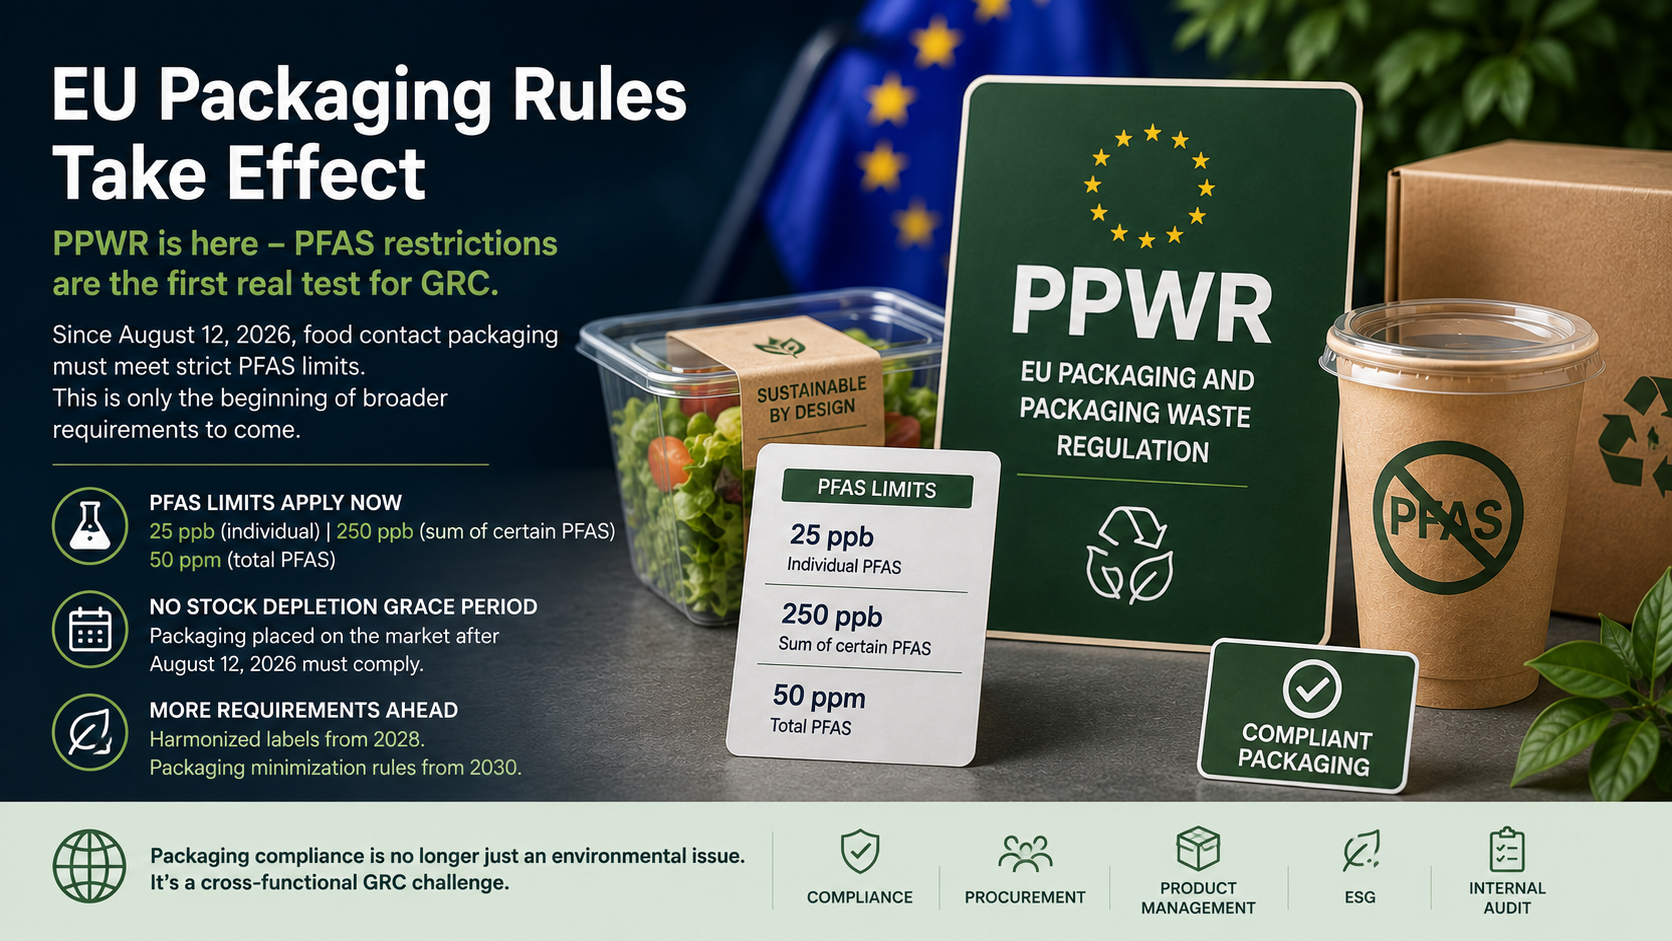
EU Packaging Regulation PPWR: Why PFAS Restrictions Are Now a GRC Topic

Since 12 August 2026, the new EU Packaging and Packaging Waste Regulation, known as the PPWR, has generally applied across the European Union. Its first immediately visible requirement is highly concrete: food-contact packaging may no longer be placed on the EU market if it reaches or exceeds certain PFAS concentration limits.

For many companies, packaging regulation may initially sound like an environmental, product or procurement issue. In reality, however, the PPWR is a classic GRC topic. It affects product design, supplier management, material data, technical documentation, conformity evidence, ESG strategy, audit readiness and market access. Any company selling packaged products in the EU will increasingly need to know not only which packaging is used, but also whether it can prove that this packaging meets the new requirements.

The PPWR entered into force on 11 February 2025 and has generally applied since 12 August 2026. It covers packaging and packaging waste regardless of material or origin and sets requirements for manufacturing, composition, reusability, recoverability and waste management.

The most urgent requirement concerns PFAS restrictions for food-contact packaging. Since 12 August 2026, such packaging may no longer be placed on the EU market if it reaches or exceeds 25 ppb for individual PFAS, 250 ppb for the sum of certain PFAS, or 50 ppm for total PFAS.

There is no general stock-depletion grace period for already manufactured food-contact packaging containing PFAS. Packaging that was placed on the market before 12 August 2026 may remain on the market. Packaging placed on the market after that date must comply with the limits.

For GRC leaders, this means that packaging compliance must become manageable across suppliers, materials, products, documentation, controls and evidence.

Why the PPWR Is More Than Environmental Regulation

The PPWR aims to reduce packaging waste, strengthen recycling, save primary resources and simplify the EU internal market through more harmonised rules. The regulation creates a framework for the entire packaging lifecycle, from product design to waste treatment. This includes restrictions on certain single-use plastics, requirements for takeaway containers, recyclability requirements and the reduction of problematic substances such as PFAS in food-contact packaging.

The GRC impact lies exactly in this breadth. Packaging is not just a shell around a product. It is part of product conformity, supply chain governance, sustainability strategy and market access. A change in material can affect suppliers, costs, shelf life, food safety, transport, brand presentation, recyclability and regulatory documentation.

This makes the PPWR a cross-functional topic. Legal teams need to understand the requirements. Procurement needs to engage suppliers. Product management needs to review packaging design and material decisions. ESG teams need reliable data for sustainability and circular economy goals. Compliance and internal audit need to ensure that evidence is available and robust.

PFAS: The First Concrete Compliance Test

PFAS are often referred to as “forever chemicals” because they are highly persistent and can accumulate in the environment and living organisms. In packaging, they have been used, among other things, for their water-, grease- and dirt-repellent properties. Examples can include coated fast-food packaging, takeaway containers, baking paper, food wrappers and other packaging with grease-barrier functionality.

The PPWR addresses this directly. Article 5 contains specific concentration limits for food-contact packaging. Market surveillance authorities can verify compliance with these PFAS limits. Since there is currently no fully harmonised EU testing methodology for PFAS in food-contact packaging, the quality of internal evidence becomes even more important.

Companies need to show which materials are used, which supplier declarations are available, which tests have been performed, which batches are affected and how decisions were documented. PFAS compliance is therefore not a one-off material check. It is a process involving supplier requests, risk assessment, testing, approval, documentation and ongoing monitoring.

Why Supplier Risk Now Becomes Packaging Risk

Many companies do not manufacture packaging themselves. They source boxes, films, labels, coatings, trays, cups, bags or composite materials from external suppliers. In many cases, packaging is further processed by converters, printers, logistics partners or co-packers.

This is exactly where the GRC risk arises. A company can only be confident that its packaging is PPWR-compliant if it understands its supply chain sufficiently. This applies not only to direct suppliers, but also to material sources, coatings, additives, recycled content and, where relevant, sub-suppliers.

In practice, requesting a generic sustainability statement will not be enough. Companies need specific, current and product-related evidence. For food-contact packaging, this is especially important: Which PFAS risks exist? Which materials and coatings are used? Which tests or certificates are available? Which supplier obligations apply? And how is it ensured that material changes are communicated?

Vendor risk management is therefore moving to a new level. It is no longer only about the financial stability, information security or data protection posture of a supplier, but also about material and product conformity.

PPWR Readiness Requires Data Governance

The PPWR shows very clearly that ESG and product regulation are becoming increasingly data-driven. Companies need to manage not only objectives, but also material data, packaging types, supplier information, technical documents and evidence.

This starts with basic questions: Which products use which packaging? Which packaging comes into contact with food? Which materials contain barrier coatings? Which suppliers provide which components? Which version of a packaging item is currently on the market? Which stocks were placed on the market before or after 12 August 2026?

This turns packaging compliance into a data and process issue. Without clear master data, ownership, versioning and evidence, a company will struggle to prove which packaging was placed on the market, when and under which conditions.

2028 and 2030: The Next Requirements Are Coming

The PFAS restrictions are only the beginning. From 2028, harmonised packaging labels are expected to help consumers sort packaging correctly. These labels will create new requirements for packaging data, material classification and design coordination.

From 2030, the PPWR will intervene even more strongly in packaging design. The regulation includes requirements for packaging minimisation. Manufacturers or importers must ensure that the weight and volume of packaging are reduced to the minimum necessary for its functionality.

For grouped packaging, transport packaging and e-commerce packaging, a maximum empty space ratio of 50 percent is also foreseen once the relevant requirements become applicable.

For companies, this means that waiting until every detail requirement becomes directly applicable is risky. Packaging design, supplier contracts, material changes, testing, labels, product approvals and data models all require lead time.

Why Excel Quickly Reaches Its Limits in Packaging Compliance

Many companies will initially try to manage PPWR requirements through Excel, supplier questionnaires and email approvals. That is understandable, but risky in the long term.

The challenge lies in the dynamics. Packaging changes. Suppliers switch materials. New tests become necessary. Authorities publish guidance. Labels are harmonised. Further requirements follow in 2030. At the same time, companies must be able to explain in an audit why a packaging item was classified as compliant and which evidence supported that decision.

If packaging data, supplier confirmations, tests, risk assessments, product approvals and remediation measures sit in separate files, an evidence problem emerges. This is typical of mature GRC topics: the challenge is not only to achieve compliance, but to make it repeatable, auditable and manageable.

What Companies Should Do Now

Companies should first clarify whether they place food-contact packaging on the EU market or use such packaging in their products. They should then assess whether PFAS-relevant materials, coatings or supplier risks exist. Crucially, this should not be treated as a one-time supplier request, but as part of an ongoing control process.

At the same time, companies should build or update their packaging inventory. Without visibility into packaging types, materials, suppliers, products and markets, a reliable PPWR roadmap is difficult to create. Documentation of the placing-on-the-market date is particularly important, because companies must distinguish between packaging placed on the market before and after 12 August 2026.

The next step is a gap assessment for upcoming requirements. 2028 and 2030 may sound far away, but they are not. Packaging changes require design decisions, supplier qualification, testing, budget, communication and operational implementation.

Conclusion: The PPWR Turns Packaging Into a GRC Data Topic

The new EU packaging rules show how strongly sustainability, product safety and compliance are converging. The PFAS restrictions for food-contact packaging are the first visible implementation test. Further requirements on labels, recyclability, recycled content, reuse and packaging minimisation will follow.

For GRC leaders, the key message is clear: packaging compliance is not an isolated environmental project. It requires clear ownership, reliable supplier data, documented risk assessments, controls, technical evidence and audit-ready decisions.

Companies that start now can reduce regulatory risk and create better transparency across products, supply chains and ESG data. Zazoon helps companies build PPWR readiness as an integrated GRC practice: from requirements and risks to suppliers, controls, evidence and audit trails.

FAQ

What is the PPWR?

The PPWR is the new EU Packaging and Packaging Waste Regulation. It replaces the previous Packaging Directive in many areas and creates a more harmonised framework for packaging and packaging waste in the EU.

Since when does the PPWR apply?

The PPWR entered into force on 11 February 2025 and generally applies from 12 August 2026. Some requirements apply later, including certain labelling and design requirements.

What changes for PFAS?

Since 12 August 2026, food-contact packaging may no longer be placed on the EU market if it reaches or exceeds certain PFAS concentration limits. The limits apply to individual PFAS, the sum of certain PFAS and total PFAS.

Is there a grace period for old stock?

There is no general stock-depletion grace period for food-contact packaging containing PFAS. Packaging placed on the market before 12 August 2026 may remain on the market. Packaging placed on the market after that date must comply with the limits.

Which companies are affected?

Affected companies include those placing packaging or packaged products on the EU market. This can include manufacturers, importers, distributors, brand owners, food companies, e-commerce providers and Swiss exporters.

Why is the PPWR a GRC topic?

The PPWR connects product compliance, ESG, supplier management, data governance, technical documentation, internal controls and audit readiness. Companies must not only understand the requirements, but also prove their implementation.

How does Zazoon support PPWR readiness?

Zazoon helps companies centrally manage requirements, risks, suppliers, controls, actions and evidence. This makes packaging compliance traceable, efficient and audit-ready.

28 July 2026 | 5 min

EU AI Act: Why Transparency Obligations Are Now a GRC Topic

The EU AI Act is becoming operational. One of the first areas companies need to address is transparency. Under Article 50, certain AI systems must clearly inform people when they are interacting with AI or when content has been generated or manipulated by AI.

This affects more companies than many expect. The rules are not limited to high-risk AI systems. Chatbots, virtual assistants, AI-generated marketing content, synthetic images, audio, video and certain deepfake use cases can all trigger transparency obligations.

For GRC teams, this marks an important shift. AI governance is no longer just about principles, policies or innovation control. It now requires concrete inventories, clear roles, risk assessments, approval processes, controls and evidence.

Transparency obligations under the EU AI Act apply to specific AI systems and use cases, including interactive AI systems such as chatbots, AI-generated or AI-manipulated content, deepfakes and certain biometric or emotion-related systems.

The core idea is simple: people should be able to recognise when they are interacting with AI or when content has been artificially generated or manipulated. In practice, however, this requires much more than adding a disclaimer.

Companies need to understand where AI is used, who owns each use case, which obligations apply, how users are informed and how implementation is documented. This makes transparency a classic governance, risk and compliance topic.

Why Article 50 Matters

Many AI Act discussions focus on high-risk AI. Article 50 shows that even companies without high-risk systems may still be affected. A customer service chatbot, an AI assistant on a website, AI-generated product images or synthetic video content may already be enough to create transparency requirements.

The aim is to prevent people from being misled. Customers, employees, partners or the public should not be left uncertain about whether they are interacting with a person or a machine, or whether a piece of content is authentic or AI-generated.

That sounds straightforward, but implementation can be complex. AI tools are often introduced quickly and decentralised across teams. Marketing uses generative content tools. Customer service pilots chatbots. HR tests AI assistants. Product teams integrate AI features. Without central oversight, companies quickly lose visibility.

Transparency Is More Than a Disclaimer

A common mistake is to treat AI transparency as a wording task. Add a label, update a footer, include a short notice and move on. That is not enough.

Transparency needs to be embedded in processes. Companies must know which AI systems are in use, what they do, who is responsible, which users are affected, whether content is generated or manipulated and which disclosure obligation applies.

A disclaimer may be the visible output. The actual GRC work happens behind the scenes: classification, approval, risk assessment, control design, documentation and review.

Chatbots and Interactive AI Systems

Chatbots and virtual assistants are among the most obvious examples. If customers interact with an AI system, they generally need to be informed that they are dealing with AI.

This is particularly relevant for customer support, online banking, insurance portals, HR helpdesks, e-commerce and SaaS platforms. The key issue is not only whether the chatbot says “I am an AI assistant”. Companies also need to ensure that the information is provided at the right moment, in a clear way and consistently across channels.

GRC teams should therefore treat chatbot deployment as a controlled process. Before go-live, the use case should be documented, transparency requirements assessed, content reviewed and ownership assigned.

AI-Generated Content and Deepfakes

The AI Act also addresses AI-generated and AI-manipulated content. This includes synthetic images, videos, audio files and deepfakes. For companies, this can affect marketing campaigns, social media, product visuals, training videos, recruitment content or public communications.

The risk is not only regulatory. It is also reputational. If customers or employees feel misled by synthetic media, trust can be damaged quickly. Transparent use of AI therefore protects both compliance and brand credibility.

Companies should define when AI-generated content needs review, approval and labelling. External agencies and service providers should also be included, because AI-generated content is often created outside the organisation.

The Role of an AI Inventory

The practical starting point is an AI inventory. Without one, companies cannot reliably identify which transparency obligations apply.

An effective AI inventory should capture the AI system, purpose, business owner, provider, user groups, data involved, output type, regulatory role, risk level, required disclosures, controls and available evidence.

For smaller and mid-sized companies, this does not need to be overly complex. But it needs to be structured, maintained and connected to responsibilities. Otherwise AI use will grow faster than governance can follow.

Conclusion: Transparency Is the First Step Toward Trustworthy AI Governance

The EU AI Act makes transparency one of the first practical AI governance obligations for many companies. Chatbots, AI-generated content and deepfakes are no longer just innovation or communication topics. They require clear ownership, controls and evidence.

For GRC leaders, this is an opportunity to build AI governance pragmatically. The first step is not a perfect AI strategy. It is visibility: knowing where AI is used, which obligations apply and how the company can prove compliance.

Zazoon supports companies in building this foundation by connecting AI use cases, risks, controls, responsibilities and evidence in one central GRC system.

FAQ

What are AI Act transparency obligations?

They are requirements that ensure people can recognise when they interact with certain AI systems or when content has been generated or manipulated by AI.

Which AI systems are relevant?

Typical examples include chatbots, virtual assistants, AI-generated content, synthetic media, deepfakes and certain biometric or emotion-related systems.

Why is transparency a GRC topic?

Because transparency requires more than a label. Companies need inventories, responsibilities, risk assessments, controls, approvals and evidence.

What should companies do first?

They should create or update an AI inventory and identify use cases that may trigger transparency obligations.

How does Zazoon help?

Zazoon helps companies manage AI use cases, risks, controls, responsibilities, vendor dependencies and evidence in one central GRC platform.

21 July 2026 | 6 min

CRA Readiness for SMEs: How ENISA’s New Maturity Model Makes Cyber Resilience More Tangible

The Cyber Resilience Act is becoming one of the most important cybersecurity and GRC topics for many companies. It particularly affects manufacturers of products with digital elements, including software, hardware, IoT products and digital components placed on the EU market.

On 13 July 2026, ENISA published the SME Cyber Resilience Maturity Assessment Model. It is designed to help small and medium-sized enterprises assess their current maturity level, identify weaknesses and strengthen their cyber resilience processes in a structured way.

For GRC leaders, this is relevant because CRA readiness goes far beyond technical product security. Risks, controls, responsibilities, documentation and vulnerability management need to be connected and managed in a traceable way.

The ENISA model is primarily aimed at SMEs that manufacture or distribute products with digital elements. It assesses five areas: Governance and Documentation, Risk Management and Security by Design, Vulnerability and Patch Management, Product Lifecycle Management, and Awareness, Competence and Skills.

ENISA distinguishes between three maturity profiles: Basic, Intermediate and Advanced. However, a high maturity level does not automatically mean CRA compliance. Instead, the model provides a practical starting point for identifying gaps and systematically improving CRA readiness.

Why the Cyber Resilience Act Is Particularly Challenging for SMEs

The Cyber Resilience Act shifts the focus from traditional IT security towards product security across the entire lifecycle. Cybersecurity must be considered from development and architecture through to updates, vulnerability handling, support and end-of-life.

For SMEs in particular, this can be challenging. Small security teams, informal processes and limited resources often make consistent regulatory evidence and documentation more difficult.

The key point is that CRA readiness is not a one-time project. Companies need repeatable processes, clear responsibilities and reliable evidence.

The Five Domains of the ENISA Model

Governance and Documentation form the foundation. Companies need to define who is responsible for product security, risk assessments, documentation, approvals and vulnerability management. Informal decisions stored in emails or tickets are unlikely to be sufficient in the long term.

Risk Management and Security by Design focus on integrating cybersecurity risks into product development and planning from the outset. Risks should be identified, assessed, treated and documented, while security requirements should become an integral part of development and release processes.

Vulnerability and Patch Management is another core area. Companies need processes to identify, assess, remediate and, where required, communicate vulnerabilities. This also includes security updates, external reporting and traceable handling of critical vulnerabilities.

Product Lifecycle Management ensures that responsibility does not end when a product is launched. Versions, components, support periods, security updates and technical dependencies need to remain transparent throughout the entire lifecycle.

Finally, ENISA also addresses Awareness, Competence and Skills. Employees in development, product management, IT, legal, support and management need to understand which CRA requirements are relevant to their work and how they should be implemented in practice.

Why the ENISA Model Is Valuable for GRC

The model makes an abstract regulatory topic more measurable. Instead of simply asking whether a company is CRA compliant, organisations can assess how mature their relevant processes are and where action is still required.

ENISA also provides an Excel-based assessment tool that allows companies to determine their maturity level and repeat self-assessments over time.

As a starting point, this is useful. In the long term, however, the resulting actions need to be connected with risks, controls, responsibilities, evidence and audits.

Awareness Is Not the Same as Readiness

The ENISA SME CRA Survey highlights a common challenge: many companies are already aware of the Cyber Resilience Act but still struggle to translate regulatory requirements into concrete processes and evidence.

The real gap lies between knowing about a regulation and being able to demonstrate that it has been implemented effectively. Technical documentation, product approvals, vulnerability management, incident response, lifecycle management and clearly defined responsibilities are particularly important.

CRA readiness should therefore not be treated as an isolated legal or security project, but as an integrated governance topic.

Why CRA Readiness Should Not End in Excel

The ENISA tool provides a useful starting point for assessing the current situation. A maturity score alone, however, does not create sustainable governance.

What matters is what happens after the assessment. Who owns each action? Which deadlines apply? Which controls ensure implementation? Where is the corresponding evidence stored, and how are changes to products, risks or suppliers taken into account?

If this information is spread across Excel files, tickets, emails and different document repositories, CRA readiness can quickly become difficult to manage.

Managing CRA Readiness with Zazoon

Zazoon helps companies connect regulatory requirements, risks, controls, tasks, responsibilities and evidence within one central GRC system.

This makes it possible to map CRA-related requirements to internal processes, structure product and cyber risks, document controls and track implementation progress in a transparent way. Third parties, technical dependencies and audit evidence can also be integrated into the overall governance approach.

For SMEs in particular, this approach is important. Regulatory expectations are increasing while resources remain limited. A guided GRC system helps turn regulatory requirements into concrete and manageable processes.

Conclusion: CRA Readiness Is Becoming More Measurable

With the SME Cyber Resilience Maturity Assessment Model, ENISA makes the Cyber Resilience Act more tangible for SMEs. Companies gain a structured approach for assessing their current maturity level and identifying existing gaps.

However, the assessment is only the beginning. The real challenge is to treat risks, implement controls, define responsibilities and maintain evidence on an ongoing basis.

Zazoon supports companies in managing these requirements in a structured way and turning CRA readiness into an integral part of everyday GRC practice.

FAQ

What is the ENISA SME Cyber Resilience Maturity Assessment Model?

The model helps small and medium-sized enterprises assess their maturity level in relation to cyber resilience and CRA-related product security processes.

Who is the model intended for?

It is primarily aimed at companies that manufacture products with digital elements and place them on the EU market. However, it can also be used by integrators, service providers and other organisations involved in the product lifecycle.

Which areas does the model assess?

It covers Governance and Documentation, Risk Management and Security by Design, Vulnerability and Patch Management, Product Lifecycle Management, and Awareness, Competence and Skills.

Does a high maturity level automatically mean CRA compliance?

No. A high maturity level does not replace legal obligations and should not be considered automatic proof of compliance.

Why is CRA readiness a GRC topic?

Because it brings together risk management, compliance, internal controls, product governance, vendor risk, audit management and evidence management.

How does Zazoon support CRA readiness?

Zazoon connects requirements, risks, controls, tasks, responsibilities and evidence in one central GRC system, making implementation more transparent and audit-ready.

7 July 2026 | 4 min

Greenwashing Risks in the Financial Sector: Why ESG Product Governance Is Becoming a GRC Issue

The European Banking Authority (EBA) has revised its Product Oversight and Governance Guidelines for retail banking products. The updated guidelines place a stronger focus on products with environmental, social or governance characteristics and on the risk of greenwashing.

For banks, financial service providers and other regulated companies, this is an important signal. ESG compliance is becoming more operational. It is no longer enough to mention sustainability features in marketing materials or product information. Companies need to demonstrate how ESG claims are created, reviewed and monitored throughout the product lifecycle.

The EBA published its revised Product Oversight and Governance Guidelines on 30 June 2026. They explicitly address ESG characteristics and greenwashing risks and are expected to apply from 11 January 2027.

For GRC leaders, this means ESG product governance needs to be more closely integrated with risk management, internal controls, approval processes, documentation and ongoing monitoring.For GRC leaders, this means ESG product governance needs to be more closely integrated with risk management, internal controls, approval processes, documentation and ongoing monitoring.

Why the EBA Is Addressing Greenwashing More Closely

ESG-related products are no longer a niche topic in the financial sector. Banks and financial service providers increasingly offer loans, accounts and other products with sustainability-related features.

At the same time, the risk is growing that ESG claims are too broad, misleading or insufficiently supported. The EBA therefore wants sustainability characteristics to be clearly defined, reviewed and monitored rather than used purely as a communication tool.

Greenwashing is consequently becoming not only a marketing or reputational risk, but also a governance and control issue.

ESG Claims Need Robust Governance

Any company describing a product as sustainable, green or ESG-oriented should be able to explain which criteria and data support that claim and who reviewed it.

Companies also need to understand where customers could misinterpret sustainability statements and which controls prevent exaggerated or unsupported claims.

These questions should not be limited to marketing approval. They need to be embedded in the organisation’s broader governance framework.

Product Governance Is Becoming an Evidence Issue

The EBA guidelines cover the entire product lifecycle, from development and approval to distribution, monitoring and adjustment.

For ESG-related products, sustainability characteristics should be clearly defined during product development. Sales and marketing communications must remain consistent with those characteristics, while complaints, market developments and regulatory changes should feed into ongoing monitoring.

This makes ESG product governance an evidence issue. In an audit or regulatory review, companies need to show that sustainability claims were part of a controlled and documented process.

What GRC Leaders Should Review Now

Companies should first identify which products use ESG characteristics or sustainability claims. They should then review who is responsible for defining, checking and approving those claims and where greenwashing, compliance or reputational risks could arise.

Controls around data quality, accuracy and documentation are equally important.

Ultimately, organisations should be able to answer one simple question: Can we demonstrate why an ESG claim was accurate, who reviewed it and which controls supported it?

Why Excel and Email Approvals Quickly Reach Their Limits

Many companies still manage product approvals, risks and evidence through Excel files, emails and separate document repositories.

With ESG claims, however, complex dependencies can quickly emerge between data sources, internal criteria, legal assessments, approvals and marketing materials.

If this information is not connected, it becomes increasingly difficult to demonstrate how decisions were made and which controls were applied.

Conclusion: Greenwashing Prevention Starts with Governance

The revised EBA guidelines make one thing clear: ESG claims need to be manageable, verifiable and supported by evidence.

Greenwashing prevention is therefore no longer just a communication task. It is becoming an important part of modern Governance, Risk and Compliance.

Companies should review whether their ESG-related product processes are sufficiently documented, controlled and audit-ready.

Zazoon helps organisations centrally manage ESG product governance, risks, controls and evidence and turn manual processes into a more robust GRC practice.

FAQ

What has the EBA published?

The EBA has published revised Product Oversight and Governance Guidelines for retail banking products. They explicitly address ESG characteristics and greenwashing risks.

Which companies are affected?

The guidelines apply to manufacturers and distributors of products within the EBA’s remit, including mortgages, personal loans, deposits, payment accounts, payment services and electronic money.

Why is this relevant for GRC?

Because ESG claims need to be supported organisationally. Companies require clear responsibilities, risk assessments, controls, approvals and evidence.

What is greenwashing in financial products?

Greenwashing occurs when sustainability claims are misleading, exaggerated, unclear or insufficiently supported.

How does Zazoon support ESG product governance?

Zazoon connects risks, controls, responsibilities, policies and evidence in one central GRC system, making ESG-related product processes more transparent and easier to audit.

30 June 2026 | 6 min

DORA Incident Reporting: Why Third Parties Are Becoming a Central Resilience Risk

DORA has moved from regulation into practice. The first assessment by the European supervisory authorities of major ICT-related incidents shows where operational resilience in the financial sector is particularly challenged: complex IT environments, cross-border dependencies and external service providers.

For GRC leaders, the message is clear. DORA compliance does not end with policies, control lists or reporting templates. What matters is whether organisations can actually manage their critical ICT service providers, outsourcing relationships, incident processes and business continuity measures. Third parties are therefore becoming a core digital resilience risk rather than just a procurement topic.

The first DORA assessment identifies 3,383 major ICT-related incidents in the EU financial sector for 2025. Around one third had cross-border effects. Particularly relevant for GRC teams is the high share of external causes: around 29 percent of major ICT incidents were attributed to third parties.

This shows that financial institutions need to manage ICT service providers, cloud providers, software partners and other critical vendors not only contractually, but also operationally and on a risk-based basis. Vendor Risk Management, Incident Management, BCM and the DORA Register of Information therefore need to be closely connected.

DORA Makes ICT Risks Measurable and Auditable

With the Digital Operational Resilience Act, the EU has created a common framework for digital operational resilience in the financial sector. Affected organisations need to demonstrate that they can identify, assess, monitor and control ICT risks.

The first incident data shows why this approach is necessary. ICT incidents are not just technical disruptions. They can affect payment processes, customer services, transactions, data availability, reporting obligations and critical business processes.

The more digital and interconnected financial institutions become, the more important robust risk management becomes. For GRC leaders, this means DORA should be treated as a management system rather than a one-time compliance project.

Third Parties Are Becoming a Central Risk Factor

One of the most important findings of the first assessment is the role of external providers. If almost one third of major ICT incidents can be traced back to third parties, a simple vendor list is no longer enough.

Financial institutions depend on cloud providers, SaaS vendors, payment service providers, data centres, IT outsourcing partners, managed service providers and data platforms. In many cases, additional dependencies exist through subcontractors or other technical components.

This makes digital supply chains more complex and harder to manage transparently. A single critical provider can affect multiple systems, processes and business areas at the same time.

Why Vendor Risk Management Is Becoming More Important Under DORA

DORA requires ICT third-party risks to be managed systematically. Organisations therefore need to understand which providers support critical or important functions, which risks are associated with them and which controls are in place.

This is not only about contracts or one-time assessments. Subcontractors, outage risks, reporting obligations, exit strategies, recurring reviews and the tracking of findings also need to be considered.

The real challenge is ongoing maintenance. Vendor information must remain connected with risks, controls, incidents, audits and business processes. Only then does an organisation gain a realistic view of its actual dependencies.

Incident Management Must Include Third Parties

Many incident management processes are well defined internally but do not sufficiently address external dependencies. Under DORA, this creates a significant risk.

If a critical ICT provider fails, an organisation needs to immediately understand which business processes and customer services are affected, which regulatory or contractual reporting obligations may apply and which workarounds or recovery plans are available.

Contacts, escalation paths and internal responsibilities also need to be defined in advance. DORA therefore increases the pressure to keep relevant information continuously up to date and auditable instead of searching for it during a crisis.

BCM and DORA Belong Together

Business Continuity Management is a central component of digital resilience. Operational disruptions often do not remain isolated but spread through systems, providers and cross-border dependencies.

A robust BCM approach under DORA should therefore also consider external dependencies, recovery times, alternative providers, escalation paths and communication processes.

The connection between Business Impact Analysis, ICT risks and Vendor Risk Management is particularly important. Only when organisations know which providers support which critical functions can realistic contingency and recovery plans be developed.

The Register of Information as a Management Tool

The DORA Register of Information is often seen primarily as a documentation requirement. Used correctly, however, it can become a central management tool for ICT third-party risks.

It creates transparency around service providers, contracts, services, critical functions, subcontractors, locations, risk assessments and responsibilities.

Its real value emerges when the register is not maintained in isolation. If it is linked with risks, controls, remediation actions, incidents and BCM scenarios, regulatory documentation becomes a practical GRC tool.

What Financial Institutions Should Do Now

The first DORA incident data shows that third-party management needs to be more closely integrated into operational resilience.

Organisations should first identify their critical ICT service providers and link them to critical or important functions. Vendor Risk Management, Incident Management and BCM should then be more closely connected.

Structured documentation of contractual and reporting obligations is equally important, as is the central management of risks, controls, actions and evidence.

Organisations that continue to manage this information across isolated Excel files, email inboxes and document folders are likely to reach their limits quickly during audits, incidents or regulatory requests.

Conclusion

The first DORA assessment makes one thing clear: ICT risks are interconnected, cross-border and heavily influenced by third parties.

For financial institutions, it is therefore not enough to document individual service providers or formally describe incident processes. What matters is the connection between Vendor Risk Management, Incident Management, BCM, the Register of Information, controls and evidence.

Organisations that manage these elements centrally can reduce regulatory complexity while improving their actual operational resilience.

Third parties are therefore not just a compliance topic. They are a central factor in digital operational resilience.

FAQ

What does the first DORA assessment show?

The assessment identifies 3,383 major ICT-related incidents in the EU financial sector for 2025. Around one third had cross-border effects, while approximately 29 percent were attributed to third parties.

Why are third parties so important under DORA?

Because many critical financial processes depend on external ICT service providers. Disruptions at cloud providers, software vendors or outsourcing partners can therefore directly affect critical business processes.

What does DORA mean for Vendor Risk Management?

Organisations need to classify ICT providers based on risk, understand critical dependencies, assess risks and continuously monitor controls and remediation actions. Subcontractors and exit strategies are also becoming more important.

What role does BCM play under DORA?

BCM needs to address external ICT dependencies more systematically. Business Impact Analysis, recovery planning and Vendor Risk Management should be connected so organisations can respond realistically to service disruptions.

What is the DORA Register of Information?

The register documents relevant ICT third-party relationships, contracts, services and dependencies. When linked with risks, controls, incidents and BCM processes, it can become an operational management tool rather than just a regulatory requirement.

What should financial institutions prioritise now?

They should focus on identifying critical ICT service providers, linking them to critical functions and integrating Vendor Risk Management, Incident Management and BCM.

16 June 2026 | 12 min

Cyber Europe 2026: Why Cyber Resilience Is Becoming a Management Priority

Cyber Europe 2026 was the eighth major European cyber crisis exercise organised by the European Union Agency for Cybersecurity, ENISA. The exercise took place on 10 and 11 June 2026 and tested how well Europe can respond in a coordinated way to large-scale cyber incidents.

The focus was on the railway and maritime sectors. The exercise simulated the handling of parallel cyber incidents affecting critical transport and logistics infrastructure. It was not only about technical defence, but also about crisis coordination, business continuity, communication with authorities, situational awareness, decision-making processes and the continuity of essential services.

Participants included European authorities, national cybersecurity bodies, operators of critical infrastructure and other organisations from the European cyber ecosystem. Switzerland also took part. Under the lead of the Federal Office for Cybersecurity, BACS, various national and cantonal authorities as well as operators of critical infrastructure participated in the exercise.

For companies, Cyber Europe 2026 sends an important signal: cyber resilience is no longer measured only by the existence of security policies. What matters is whether organisations can remain operational during an incident, make clear decisions, coordinate their response and document their actions in a reliable way.

Cyber Europe 2026 was a Europe-wide cyber crisis exercise organised by ENISA, with a focus on railway and maritime transport.

The exercise tested responses to parallel cyber incidents, coordination between authorities and operators, and the ability to maintain essential services.

Switzerland participated under the lead of BACS. National and cantonal authorities as well as operators of critical infrastructure were involved.

For companies, the exercise shows that cyber resilience goes far beyond IT security. Incident response, business continuity management, crisis communication, vendor management and management responsibility must work together.

In the context of NIS2, critical infrastructure and rising cyber risks, operational evidence is becoming increasingly important. Companies must not only plan, but also exercise, document and improve.

What Is Cyber Europe 2026?

Cyber Europe is a regular European cyber crisis exercise organised by ENISA. It brings together authorities, critical sectors and cybersecurity organisations. The goal is to simulate realistic cyber crises and test how well collaboration, escalation and crisis response work in practice.

Cyber Europe 2026 focused on transport networks, especially rail and maritime infrastructure. Both sectors are highly connected, internationally dependent and essential for the economy, supply chains and mobility. A cyberattack on such infrastructure can have consequences far beyond a single company.

For this reason, the exercise was not designed as an isolated technical test. It aimed to show how organisations work together under pressure, exchange information, make decisions and keep operations as stable as possible.

What Was Tested During Cyber Europe 2026?

The exercise centred on several parallel cyber incidents. Such scenarios are particularly demanding because they put organisations under pressure at the technical, operational and strategic levels at the same time.

The exercise tested, among other things, how quickly incidents are detected and assessed, how information flows between the parties involved, how crisis teams make decisions and how essential services can be maintained despite cyberattacks.

Business continuity was also a key element. A cyber incident is not just an IT problem when timetables, logistics processes, port operations, communication systems or safety-related operational processes are affected. Companies need to know which processes are critical, which dependencies exist and which alternatives are available in an emergency.

Another focus was coordination. Cyber crises can quickly cross organisational and national boundaries. Operators, service providers, authorities, regulators, crisis teams and communication teams must work together under time pressure. In real crises, these interfaces are often the biggest weakness.

Why the Railway and Maritime Sectors Were in Focus

Railway and maritime transport are central components of European mobility and supply chains. They connect passenger transport, goods flows, ports, industry, energy supply and international trade routes.

At the same time, these sectors are becoming increasingly digital. Operational control systems, communication networks, booking platforms, port management, logistics data, sensors and automated processes increase efficiency, but also create new attack surfaces.

A successful cyberattack can therefore have far-reaching consequences. It can delay supply chains, disrupt passenger transport, increase safety risks and damage public trust.

Cyber Europe 2026 therefore illustrates a challenge that applies to many critical sectors: the more connected organisations become, the more important robust cyber resilience, clear responsibilities and tested crisis processes become.

Why Switzerland’s Participation Matters

Switzerland participated in Cyber Europe 2026 and tested its cyber resilience in the railway and maritime sectors. The exercise was led in Switzerland by the Federal Office for Cybersecurity, BACS. National and cantonal authorities as well as operators of critical infrastructure were involved.

This is relevant for two reasons. First, cyber risks are cross-border by nature. Even though Switzerland is not a member of the EU, it is closely connected to European transport, energy, financial and supply chains. An incident in a neighbouring country can affect Swiss organisations, and vice versa.

Second, Switzerland’s participation shows that cyber resilience is not only a matter for national authorities. It is created through cooperation between the state, the private sector, critical operators and specialised service providers. In major incidents, it matters whether this cooperation has already been tested.

For Swiss companies, the message is clear: cyber crises must not only be prepared for technically. They require crisis leadership, reporting channels, roles, supplier contacts, recovery plans and documented decision-making processes.

Cyber Europe 2026 and NIS2: What Companies Should Take Away

Cyber Europe 2026 fits directly into current developments around NIS2. The directive strengthens requirements for cybersecurity, risk management, incident reporting and management responsibility in important and essential entities.

The exercise shows what matters in practice. Companies must not only meet requirements, but also demonstrate that their processes work during an actual incident. This is especially relevant for incident response, business continuity management, crisis communication and the management of external dependencies.

NIS2 is becoming increasingly operational. A policy alone is not enough. A company must know who makes decisions during an incident, which systems are critical, which service providers need to be involved, which reporting deadlines apply and which evidence must be available afterwards.

Cyber Europe 2026 makes one thing clear: cybersecurity readiness must be exercised. Only then can companies see whether roles are clear, escalation paths work and measures are effective in practice.

Why Cyber Resilience Is More Than IT Security

Cyber resilience describes an organisation’s ability to prevent, detect, manage and recover from cyber incidents. This goes far beyond traditional IT security.

Technical protection measures remain important. But during a crisis, organisational factors are just as decisive. These include clear responsibilities, fast decision-making, crisis communication, emergency processes, supplier coordination and the ability to continue critical business processes.

A company can be technically well positioned and still fail during a crisis if it is unclear who decides, who communicates or which systems need to be restored first.

Conversely, an organisation with strong governance can respond faster, limit damage and learn from incidents. Cyber resilience is therefore a management topic and a central part of modern GRC structures.

The Role of Business Continuity Management

Business continuity management, or BCM, plays a central role in cyber crises. It answers the question of how critical processes can continue when systems, service providers or locations fail.

Cyber Europe 2026 shows that BCM should not be viewed separately from cybersecurity. A cyber incident can disrupt business processes just as severely as a natural disaster, power outage or supply chain disruption.

Companies should therefore review whether their BCM plans are realistic from a cyber perspective. Are recovery priorities defined? Are critical processes known? Are dependencies on service providers documented? Are alternative communication channels available? Have crisis roles been tested?

BCM proves its value not on paper, but in exercises. Companies that regularly simulate cyber crises identify weaknesses before a real incident exposes them.

Incident Response: From Plan to Tested Reaction

Many companies have incident response plans. The decisive question is whether these plans work under pressure.

Cyber Europe 2026 shows that incident response is dynamic. Information is incomplete, decisions must be made quickly and multiple stakeholders are involved at the same time. This is why a static process document is not enough.

Effective incident response requires clear roles, defined escalation levels, communication rules, technical analysis capabilities and links to management, legal, data protection, communications and business departments.

Post-incident review is just as important. Every incident and every exercise should be documented and evaluated. Which decisions were made? Which measures worked? Where were there delays? Which controls need to be improved?

This turns incident response into a continuous improvement process.

Suppliers and External Dependencies as a Risk Factor

Cyber crises rarely affect only one organisation. Many critical processes depend on IT service providers, cloud providers, software vendors, network operators, logistics partners or specialised platforms.

Such dependencies are particularly important in the railway and maritime sectors. But the same principle applies in other industries: companies that do not know their critical third parties will struggle to respond quickly and effectively during an incident.

Companies should therefore know which service providers are relevant for critical processes, which contact and escalation channels exist, which contractual obligations apply and which evidence is available.

Vendor risk management is becoming a permanent part of cyber resilience. It is not enough to assess suppliers once. Dependencies must be monitored continuously and included in crisis exercises.

Why Evidence and Documentation Are Critical

After a cyber crisis, it is not only important what was done. It is also important whether the company can show what was done in a reliable and traceable way.

Documentation is therefore not an administrative side issue. It is central for audits, regulatory inquiries, internal lessons learned, insurance claims, customer communication and possible legal assessments.

In an emergency, companies must be able to trace when an incident was detected, who was informed, which decisions were made, which measures were implemented and which systems were affected.

Cyber Europe 2026 shows that evidence is part of resilience. Companies that cannot document their response will later struggle to demonstrate effectiveness, due care and improvement.

What Companies Should Do Now

Companies should use Cyber Europe 2026 as an opportunity to review their own crisis readiness. The most important step is an honest assessment of the current state.

Are critical processes known? Are incident response plans up to date? Are roles and escalation paths clear? Have crisis exercises been conducted? Are suppliers integrated into emergency processes? Is there a connection between cybersecurity, BCM, risk management and management reporting?

Tabletop exercises are particularly useful. They allow organisations to run through a realistic crisis scenario without affecting production systems. Such exercises quickly show whether responsibilities are clear and whether decision-making paths work.

Companies should also review their evidence management. Risks, controls, measures, incidents, exercises and lessons learned should not be scattered across individual files, but managed in a structured way.

Common Weaknesses in Cyber Crises

Many organisations underestimate organisational weaknesses. In practice, crisis response rarely fails only because of missing technology. More often, the problem lies in unclear responsibilities, outdated contact lists, slow escalation, incomplete situational awareness or inconsistent communication.

Another weakness is the separation of IT and business processes. If technical teams do not know which processes are business-critical, recovery priorities may be set incorrectly.

External dependencies are also often considered too late. If a critical service provider cannot be reached or contractual reporting channels are unclear, the company loses valuable time.

Cyber Europe 2026 therefore shows that resilience is not created by individual measures. It is created through the interaction of people, processes, technology, governance and practice.

Conclusion

Cyber Europe 2026 was an important practical test of Europe’s cyber resilience. The focus was on railway and maritime transport, two sectors whose disruption can have far-reaching consequences for mobility, supply chains and public safety.

The exercise clearly shows that cybersecurity is no longer a purely technical task. Companies must be able to manage cyber incidents organisationally, operationally and strategically. This includes incident response, business continuity management, crisis communication, vendor management, management responsibility and reliable evidence.

For companies in Europe and Switzerland, the most important lesson is this: cyber resilience must be exercised. Plans, policies and controls are necessary, but only realistic exercises show whether they work in practice.

Cyber Europe 2026 is not just an isolated public-sector event. It is a clear signal to all organisations: the next stage of cybersecurity is operational resilience.

FAQ on Cyber Europe 2026

What is Cyber Europe 2026?

Cyber Europe 2026 was a Europe-wide cyber crisis exercise organised by ENISA. Its goal was to test Europe’s collective response capability during major cyber incidents and strengthen the cyber resilience of essential services.

When did Cyber Europe 2026 take place?

Cyber Europe 2026 took place on 10 and 11 June 2026.

Which sectors were in focus?

The exercise focused on the railway and maritime sectors. It tested the handling of cyber incidents that could affect transport and logistics infrastructure.

Did Switzerland participate in Cyber Europe 2026?

Yes. Switzerland participated under the lead of the Federal Office for Cybersecurity, BACS. National and cantonal authorities as well as operators of critical infrastructure were involved.

What was tested during Cyber Europe 2026?

The exercise tested incident response, crisis coordination, business continuity, information exchange, communication with authorities and the ability to maintain essential services despite cyber incidents.

Why is Cyber Europe 2026 relevant for companies?

The exercise shows that cyber resilience does not depend only on technical security measures. Companies must also be organisationally prepared, have clear roles, coordinate incidents and document their response.

What does Cyber Europe 2026 have to do with NIS2?

NIS2 strengthens requirements for cybersecurity, risk management, incident reporting and management responsibility. Cyber Europe 2026 shows in practical terms why these capabilities are essential in realistic crisis scenarios.

Why does business continuity management play such an important role?

Cyber incidents can interrupt critical business processes. Business continuity management helps companies maintain essential processes even during system outages, attacks or supplier disruptions.

What should companies do after Cyber Europe 2026?

Companies should review their incident response plans, BCM processes, crisis roles, supplier dependencies and evidence management. Regular tabletop exercises and realistic crisis simulations are especially valuable.

What is the main lesson from Cyber Europe 2026?

The main lesson is that cyber resilience is not created by policies alone. Companies must exercise their crisis capabilities, clarify responsibilities, understand dependencies and act in a traceable way during an incident.

9 June 2026 | 12 min

ENISA NIS360 2026: Why NIS2 Maturity Assessment Is Now a GRC Priority

With NIS360 2026, ENISA has published the third edition of its report on the cybersecurity maturity of critical EU sectors. The report assesses how mature individual sectors of high criticality are in managing cyber risks and how critical they are to society, the economy and public safety.

For companies, this is more than just another industry analysis. NIS360 indicates where NIS2 implementation is heading: away from simply determining whether an organisation falls within the scope of NIS2 and towards measurable cybersecurity maturity. The decisive question is no longer only whether a company is subject to NIS2. What increasingly matters is how transparently and systematically risks, controls, responsibilities and evidence are managed.

This moves NIS2 even further into the core of governance, risk and compliance. Companies that do not know their maturity level will struggle to set priorities, explain weaknesses clearly and meet audit or regulatory requirements without significant effort.

ENISA NIS360 2026 assesses the cybersecurity maturity and criticality of sectors of high criticality under NIS2.

The report shows that cybersecurity maturity in Europe is improving, but significant differences between sectors remain.

The comparison between criticality and maturity is particularly relevant. Sectors with high importance but comparatively low maturity are likely to face increased attention.

For GRC professionals, this means that NIS2 is becoming increasingly measurable. Maturity models, control evidence, risk registers, responsibilities and management reporting are becoming more important.

Companies should not treat their NIS2 implementation merely as a compliance project, but as a permanent governance framework for cyber resilience.

What Is ENISA NIS360 2026?

ENISA NIS360 is a report published by the European Union Agency for Cybersecurity. It assesses the cybersecurity maturity of sectors that fall within the sectors of high criticality covered by the NIS2 Directive.

The assessment goes beyond technical security. ENISA considers the entire sectoral context, including competent authorities, affected entities, regulatory requirements, operational capabilities, maturity levels, dependencies and societal importance.

NIS360 therefore provides an overview of how well individual sectors are prepared for cyber risks. At the same time, the report identifies areas that are particularly critical because disruptions could have significant consequences for society and the economy.

For companies, this is important because it provides an indication of the expectations that regulators, customers, auditors and business partners may increasingly impose in the future.

Why NIS360 Is Relevant for Companies

At first glance, NIS360 assesses entire sectors rather than individual companies. Nevertheless, the report is highly relevant to organisations.

It shows which industries are receiving greater regulatory, political and operational attention. When a sector is considered particularly critical, pressure on individual companies within that sector generally increases as well. This does not only affect operators of critical infrastructure, but also service providers, suppliers and digital partners.

Companies therefore need to prepare for increasing demand for evidence. Simply describing individual security measures is no longer sufficient. Organisations are increasingly expected to provide a clear picture of how cyber risks are managed, which controls are effective and how their cybersecurity maturity improves over time.

NIS360 therefore makes one point particularly clear: NIS2 compliance is not a one-time status. It is becoming a continuous maturity process.

From NIS2 Compliance to Cybersecurity Maturity

Many companies initially approached NIS2 by asking one question: Are we affected or not? This question remains important, but it is no longer sufficient.

The next phase of NIS2 implementation is about maturity and effectiveness. Companies must not only understand the requirements but also demonstrate how these requirements have been implemented in practice.

This includes clear governance structures, documented risks, defined measures, effective controls, verifiable evidence and regular management reporting. These elements determine whether an organisation can credibly demonstrate its cybersecurity maturity.

A low maturity level does not automatically mean that a company is non-compliant. However, it highlights where gaps exist, where priorities need to be set and where risks may not yet be managed adequately.

Why Maturity Assessment Is Becoming Critical for GRC Professionals

GRC professionals increasingly need to build bridges between regulatory requirements, technical security measures, operational risks and management decisions.

NIS360 shows that cybersecurity cannot be viewed in isolation. Cyber risks affect supply chains, business processes, crisis management, responsibilities, internal controls and strategic investments.

A maturity assessment helps bring these areas together in a structured way. It answers key questions:

How well prepared is the company for cyber risks?

Which controls are in place, and how effective are they?

Which risks have been accepted, mitigated or remain unresolved?

Which measures should be prioritised?

What evidence is available in the event of an audit?

How does the organisation’s maturity develop over time?

This makes maturity assessment a management and governance tool. It makes progress visible and helps organisations justify investments more effectively.

What Companies Can Learn from NIS360 2026

The key message from NIS360 2026 is clear: cybersecurity maturity is improving, but not evenly. Some sectors are already comparatively advanced, while others remain vulnerable despite their high criticality.

For companies, this means that their own maturity should not only be assessed internally. It also needs to be understood within the context of the relevant industry. A company operating in a particularly critical sector is likely to face stricter expectations than one operating in a less sensitive environment.

This is not only about technical security measures. The decisive factor is whether cybersecurity is embedded within the organisation. Are responsibilities clearly defined? Are risks assessed regularly? Can measures be tracked? Are incidents managed systematically? Is senior management involved? Are supplier risks considered?

Companies that cannot answer these questions clearly have a governance problem, even if individual technical controls are already in place.

The Role of Governance in NIS2

NIS2 makes cybersecurity a management responsibility. This means that cyber risks cannot remain solely within the IT department. They must become part of corporate governance and management.

Governance provides the framework that defines responsibilities, decision-making processes and control mechanisms. Without clear governance, typical weaknesses emerge: unclear responsibilities, fragmented documentation, incomplete tracking of measures and insufficient transparency for management.

Effective NIS2 governance should define who is responsible for cyber risks, how risks are assessed, which controls apply, how measures are prioritised and how progress is reported.

NIS360 reinforces this perspective. Organisations that want to demonstrate their maturity need more than individual security projects. They need a system for managing, monitoring and continuously improving cybersecurity.

Why Evidence Is Becoming a Bottleneck

Many companies already have security policies, risk assessments, training programmes, technical controls and incident management processes. The problem is often not that nothing exists. The problem is being able to prove it.

Information is frequently distributed across different tools, Excel files, email threads, ticketing systems, audit folders and departments. In day-to-day operations, this may work to some extent. During an audit or regulatory request, however, it can quickly become a major challenge.

NIS2 and the associated focus on maturity increase the pressure for centralised evidence management. Companies need to demonstrate which risks have been assessed, which measures resulted from those assessments, who is responsible, which controls have been implemented and when those controls were reviewed.

Evidence therefore becomes a fundamental component of cybersecurity maturity. Without evidence, maturity remains merely a claim.

Which Areas Companies Should Review Now

Companies should use NIS360 2026 as an opportunity to systematically assess their NIS2 readiness. This should go beyond a legal assessment of whether the company falls within the scope of NIS2. The more important question is how robust the organisation’s governance and management framework actually is.

Five areas are particularly important:

First: governance and responsibilities. Companies should clearly define who monitors cyber risks, who approves measures and how senior management is involved.

Second: risk management. Cyber risks should be assessed regularly, prioritised and linked to specific measures.

Third: control management. Security measures must not only exist; they need to be documented transparently and reviewed regularly.

Fourth: incident management and crisis preparedness. Companies should understand how they detect, assess, report and follow up on incidents.

Fifth: supplier and third-party risks. Many cyber risks originate outside the organisation itself. Critical service providers, dependencies and supporting evidence therefore need to be integrated into NIS2 governance.

What an Effective NIS2 Maturity Process Needs to Achieve

A strong maturity process begins with transparency. Companies need to understand which requirements apply, which risks exist and which controls are already in place.

The next step is assessment. Not every gap has the same level of criticality. A maturity model helps organisations classify weaknesses and set priorities. The focus should not only be on formal compliance, but also on actual effectiveness.

Connecting information is equally important. Risks, controls, measures, responsibilities and evidence must not be managed in isolation. Only when these elements are linked can an organisation develop a realistic picture of its cybersecurity maturity.

Finally, regular updates are essential. Cyber risks, threats, systems, supply chains and regulatory expectations continuously change. A maturity assessment is therefore not a one-time check, but part of a continuous improvement process.

Common Mistakes in NIS2 Implementation

One common mistake is focusing exclusively on requirement catalogues. Companies may check which requirements exist while losing sight of effectiveness, prioritisation and evidence.

Another mistake is separating compliance from cybersecurity. If compliance teams only document requirements while IT teams only implement technical measures, there is often no common governance framework. NIS2, however, requires an integrated approach combining risk, controls, technology, organisation and management.

Decentralised documentation is another problem. When risks, measures and evidence are distributed across multiple locations, it becomes difficult to establish a reliable picture of maturity.

A fourth mistake is underestimating supplier risk. Critical digital dependencies in particular can significantly affect an organisation’s own cybersecurity maturity. Companies that do not understand these dependencies cannot credibly manage their cyber resilience.

Why NIS2 Maturity Assessment Also Matters for Companies Not Directly Subject to NIS2

Not every company falls directly within the scope of NIS2. Nevertheless, NIS360 2026 can also be highly relevant for organisations that are only indirectly affected.

Many companies are part of supply chains, provide services to regulated customers or offer digital services. In such cases, customers may increasingly demand evidence of cybersecurity maturity even when there is no direct legal obligation.

This is particularly relevant for IT service providers, cloud providers, software companies, consultancies, managed service providers and specialised suppliers. Companies serving critical customers will increasingly need to explain how they manage cyber risks.

NIS2 therefore extends beyond its direct legal scope. Its requirements are increasingly finding their way into contracts, supplier assessments, procurement processes and customer audits.

Conclusion

ENISA NIS360 2026 clearly shows that NIS2 is evolving from a regulatory obligation into a measurable maturity framework for cybersecurity and GRC.

For companies, this means that cybersecurity can no longer be treated solely as a technical issue or temporary project. What increasingly matters is whether risks, controls, responsibilities and evidence can be managed centrally and systematically.

The most important step is transparency. Companies need to understand where they currently stand, which gaps exist and which measures will have the greatest impact. Maturity assessment provides the foundation for this.

Companies that treat NIS2 merely as a checklist are likely to face increasing pressure over time. Organisations that understand NIS2 as a governance and maturity process can connect regulatory requirements, cyber resilience and management oversight in a meaningful way.

FAQ: ENISA NIS360 2026 and NIS2 Maturity

What is ENISA NIS360 2026?

ENISA NIS360 2026 is a report published by the European Union Agency for Cybersecurity. It assesses the cybersecurity maturity and criticality of sectors of high criticality covered by the NIS2 Directive.

Why is NIS360 important for companies?

The report shows how expectations around cybersecurity and NIS2 implementation are evolving. For companies, it demonstrates that maturity, evidence and governance structures are becoming increasingly important.

What does cybersecurity maturity mean?

Cybersecurity maturity describes how advanced an organisation or sector is in managing cyber risks. It includes risk management, controls, processes, responsibilities, incident management and continuous improvement.

How is NIS360 related to NIS2?

NIS360 examines sectors that fall within the sectors of high criticality covered by the NIS2 Directive. The report helps organisations better understand the maturity and criticality of these sectors.

Why is an NIS2 gap analysis not enough?

A gap analysis identifies which requirements have not yet been fulfilled. However, it often provides limited information about how effective controls are, how well risks are managed and whether evidence is available in an audit-ready format.

What role does governance play in NIS2?

Governance ensures that responsibilities, decision-making processes, controls and reporting are clearly defined. Without effective governance, NIS2 often remains an isolated technical project rather than becoming a manageable business process.

Why is evidence so important?

Evidence demonstrates that risks have been assessed, measures have been implemented and controls have been reviewed. Without evidence, it is difficult to credibly demonstrate maturity to management, auditors, customers or regulators.

Does NIS2 also affect suppliers?

Yes. Suppliers and service providers play an important role. Even if a company does not fall directly within the scope of NIS2, it may be indirectly affected through customer requirements, contractual obligations or audits.

What should companies do now?

Companies should assess their NIS2 maturity, identify key risks, clarify responsibilities, document controls, structure their evidence and incorporate supplier risks into their governance framework.

Is NIS2 compliance a one-time project?

No. NIS2 compliance is a continuous process. Threats, systems, supply chains and regulatory expectations are constantly evolving. Cybersecurity maturity therefore needs to be assessed and improved on a regular basis.

19 May 2026 | 10 min

AI Risk Becomes a Supervisory Topic: What the BaFin Warning Means for DORA, BCM and Vendor Risk

In mid-May, BaFin made it clear that cyber risks for financial institutions continue to increase. One point is particularly relevant: attackers are using artificial intelligence more often to identify vulnerabilities faster, prepare attacks more effectively and target IT systems with greater precision.

For banks, insurers and other regulated companies, this is more than a technical warning. If AI makes attacks faster and more scalable, the requirements for risk management, business continuity, third-party oversight and evidence documentation also increase. In short: AI risk is becoming a supervisory topic.

This does not only affect companies that use AI themselves. It also affects companies whose IT, suppliers, cloud services or software products may become more vulnerable to AI-driven attacks. This is exactly where DORA, BCM and vendor risk management come into play.

AI is changing the cyber threat landscape. Attackers can identify vulnerabilities faster, create more realistic phishing messages and automate attacks more effectively. This increases the pressure on companies to detect and close security gaps more quickly.

For financial institutions, this is especially relevant because DORA makes digital operational resilience a binding requirement. Companies need to manage and document risks, ICT systems, service providers, incidents and recovery processes more effectively.

Business continuity management and vendor risk management are also becoming more important. An AI-driven cyberattack rarely affects only one system. It can impact service providers, critical processes, data, customer communication and ongoing operations at the same time.

Why AI increases cyber risks

Cyberattacks are not new. What is new is the speed and quality with which attackers can use AI.

In the past, many steps had to be performed manually: analysing systems, searching for vulnerabilities, preparing attacks, writing phishing messages or adapting technical attack patterns. With AI, many of these steps can be accelerated or partly automated.

This does not mean that every attack will automatically be successful. But it does mean that companies must expect more attempts, better prepared attacks and shorter response windows.

Typical risks include:

  • faster identification of vulnerabilities in IT systems
  • more realistic phishing and social engineering attacks
  • automated analysis of publicly available information
  • more targeted attacks on employees, service providers or executives
  • faster adaptation of attack methods
  • higher pressure on security, IT and incident teams

For GRC teams, the key point is this: AI-driven cyberattacks are not just an IT security issue. They affect governance, risk, compliance, suppliers, emergency planning and management reporting.

What this has to do with DORA

DORA requires financial institutions to manage their digital operational resilience systematically. At its core, DORA is about ensuring that companies remain operational even during IT disruptions, cyberattacks or problems with external service providers.

AI-driven attacks increase pressure in exactly this area.

Companies need to know which ICT systems are critical, which risks exist, which controls are in place, which service providers are involved and which measures are triggered in the event of an incident. At the same time, they need to prove that this information is up to date and manageable.

DORA is therefore not only about technical security. It requires a reliable management system for digital risks.

In practice, this means:

  • ICT risks must be assessed regularly
  • critical systems and processes must be known
  • security measures must be documented and reviewed
  • incidents must be detected, assessed and reported
  • service providers must be managed according to risk and criticality
  • recovery and emergency processes must work in practice

If AI makes attacks faster, the quality of these processes becomes more important. Companies cannot afford to start searching for information only once an incident has already happened.

Why BCM is becoming more important

Business continuity management often only becomes visible when something fails. That is exactly the problem.

An AI-driven cyberattack may not only affect individual IT systems. It can also disrupt critical business processes, customer communication, data access or external service providers.

In that situation, having an emergency plan in a folder is not enough. Companies need to know:

  • Which processes are truly critical?
  • Which systems support these processes?
  • Which service providers are involved?
  • What alternatives exist if a system or provider fails?
  • Who makes decisions during a crisis?
  • How quickly do systems need to be restored?
  • What internal and external communication is required?

BCM therefore needs to be more closely connected with cyber risk, incident management and vendor risk management. Only then can companies gain a realistic view of their actual resilience.

Why vendor risk management is critical

Many companies no longer operate their most important systems entirely by themselves. They rely on cloud providers, software solutions, outsourcing partners, managed services and specialised IT providers.

This is normal and often efficient. But it changes the risk profile.

If a critical service provider is attacked, the company itself may still be affected. If a software provider has a vulnerability, it can create risk for many customers. If a cloud service fails, core business processes may come to a halt.

AI-driven attacks make this problem more serious because attackers can analyse supply chains more precisely and identify weak points faster.

That is why a simple supplier list is no longer enough. Companies need structured vendor risk management. They need to know which providers are critical, what services they deliver, which data is affected, which security requirements apply and which evidence is available.

Particularly important are:

  • criticality assessments of service providers
  • documentation of ICT dependencies
  • security requirements in contracts
  • regular supplier assessments
  • evidence of controls and certifications
  • exit strategies for critical providers
  • connection with BCM and incident management

Vendor risk is therefore not just a procurement topic. It is a central part of cyber resilience.

The real problem: information is often scattered

Many companies already have much of the information they need. It is simply not available where it is needed in an emergency.

Risks are documented in spreadsheets. Supplier information sits with procurement. Emergency plans are maintained separately. Incidents are handled in a ticketing system. Controls are documented in audit files. Evidence is stored in folders. Management reports are created manually.

As long as nothing happens, this may seem manageable. During a cyber incident, it becomes a problem.

At that point, companies need to know quickly which systems are affected, which processes are critical, which service providers are involved, which reporting obligations apply and which measures have already been planned or implemented.

If this information is scattered, companies lose time. And in a cyberattack, time is one of the most important factors.

What companies should do now

Companies do not need to launch a massive new programme immediately. But they should review their existing processes in a targeted way.

The first step is transparency. Which critical systems, processes and service providers exist? Which risks are known? Which measures are already in progress? Where is evidence missing?

The second step is connection. Risks, controls, suppliers, incidents and BCM plans should not be managed in isolation. They need to be linked.

The third step is auditability. Supervisors, auditors and management need clear answers. Not at some point in the future, but quickly and reliably.

For many companies, these questions are especially important:

  • Are AI-related cyber risks included in risk management?
  • Are critical ICT systems and service providers fully documented?
  • Are BCM plans connected to real system and supplier dependencies?
  • Are there clear processes for cyber incidents and reporting obligations?
  • Can controls, measures and evidence be found quickly?
  • Is there up-to-date reporting for management and supervisors?

These questions are simple. But they quickly show whether a company is truly in control.

The role of Zazoon GRC

Zazoon GRC helps companies manage cyber risks, DORA requirements, BCM, vendor risk and evidence centrally.

Instead of maintaining risks, controls, service providers, incidents and measures in different tools, companies can connect this information in one shared GRC structure. This creates a clearer picture: Which risks affect which systems? Which providers are critical? Which measures are still open? Which evidence is available? Which requirements are being fulfilled?

This transparency is especially important for AI-driven cyber risks. The faster the threat landscape changes, the more important up-to-date data, clear responsibilities and traceable processes become.

Zazoon helps companies view compliance not as an isolated obligation, but as a foundation for better resilience and better decision-making.

Conclusion: AI makes cyber risk faster, GRC needs to become more structured

The BaFin warning makes one thing clear: AI is changing the cyber threat landscape. Attacks can become faster, more targeted and more scalable. For regulated companies, this increases pressure on DORA, BCM, vendor risk and incident management.

The answer is not more manual documentation. The answer is better structure.

Companies need to know which risks exist, which systems are critical, which service providers are involved, which measures are effective and which evidence is available. This is the core of modern GRC processes.

AI risk is therefore no longer a future topic. It is a current supervisory topic and a clear reason to connect digital resilience, third-party oversight and business continuity more closely.

FAQ

What does AI risk mean in cybersecurity?

AI risk describes risks that arise from or are amplified by the use of artificial intelligence. In cybersecurity, this mainly means that attackers can use AI to identify vulnerabilities faster, create more realistic phishing attacks or automate attack processes more effectively.

Why is the BaFin warning important for companies?

BaFin makes it clear that AI-driven cyberattacks are not only a technical problem. They can threaten the stability of companies, the availability of services and digital resilience. For regulated companies, this increases the pressure to manage and document cyber risks more effectively.

What does AI risk have to do with DORA?

DORA requires financial institutions to manage digital risks in a structured way. If AI makes cyberattacks faster and more complex, companies need better control over their ICT risks, controls, incidents, service providers and recovery processes.

Why is BCM important for AI-driven cyberattacks?

Business continuity management ensures that critical business processes can continue or be restored quickly during disruptions. In an AI-driven cyberattack, one incident can affect several systems, providers and processes at the same time. That is why BCM must be closely connected with cyber risk and incident management.

What role does vendor risk management play?

Many cyber risks do not arise only inside the company. They can also come from service providers, cloud providers or software suppliers. Vendor risk management helps companies identify critical providers, assess risks and document security requirements in a traceable way.

Do companies now need separate AI risk programmes?

Not necessarily. The first step should be to integrate AI-related cyber risks into existing GRC, DORA, BCM and vendor risk processes. What matters most is that risks, controls, measures and evidence can be managed centrally.

Is a technical security solution enough?

No. Technical security solutions are important, but they are not enough on their own. Companies also need clear responsibilities, documented processes, supplier oversight, emergency plans, incident management and reliable evidence.

How does Zazoon GRC support AI risk management?

Zazoon GRC helps companies manage risks, controls, measures, suppliers, incidents and evidence centrally and connect them with each other. This makes it easier to understand where risks arise, which measures are effective and which regulatory requirements are being fulfilled.

11 May 2026 | 17 min

NIS2, DORA, CRA: Three Regulations, One Common Challenge

Why companies need integrated GRC processes instead of parallel compliance projects

NIS2, DORA and the Cyber Resilience Act are among the most important European regulations for cybersecurity, digital resilience and risk management. At first glance, they address different target groups: NIS2 applies to many essential and important entities, DORA focuses on the financial sector and its ICT service providers, while the Cyber Resilience Act places stronger obligations on manufacturers and providers of digital products.

In practice, however, it quickly becomes clear that these three regulations have more in common than many companies initially assume. They require structured risk management, clear responsibilities, documented measures, functioning reporting processes, controlled supply chains and reliable evidence.

The real problem arises when companies treat each regulation as a separate project. One project is created for NIS2, another for DORA, another for the CRA, alongside existing ISO 27001, data protection or audit initiatives. Each team works with its own lists, controls, evidence and responsibilities. This leads to duplicated work, inconsistent information and unnecessary complexity.

This is exactly why companies do not need another compliance silo. They need integrated GRC processes. By connecting risks, controls, suppliers, incidents, assets, measures and evidence in one central system, companies can meet regulatory requirements more efficiently while strengthening their cyber resilience.

NIS2, DORA and the CRA differ in terms of target groups, scope and specific obligations. What they have in common, however, is that they require companies to strengthen cyber resilience, improve risk management and maintain reliable documentation.

Companies that implement each regulation separately quickly create parallel processes. Risks are recorded multiple times, controls are documented twice, suppliers are assessed differently and evidence is distributed across different systems. This increases effort without necessarily improving security or governance.

An integrated GRC approach solves this problem. Requirements, risks, controls, measures, suppliers, incidents and evidence are managed in one shared system and linked with each other. This makes it much easier to manage NIS2, DORA, CRA and other standards such as ISO 27001, GDPR or BSI IT-Grundschutz efficiently.

Three regulations with different priorities

NIS2: Cybersecurity becomes a leadership responsibility

The NIS2 Directive significantly expands the number of regulated companies. It affects many organisations in essential and important sectors, including energy, transport, healthcare, digital infrastructure, public administration, manufacturing, food, chemicals and digital services.

At its core, NIS2 focuses on risk management, technical and organisational security measures, reporting obligations and the responsibility of senior management. It makes one thing clear: cybersecurity is not just an IT department issue. It is a management responsibility with direct governance relevance.

Companies must not only implement security measures. They must also be able to demonstrate that these measures are appropriate, documented and effective. This is where GRC becomes essential.

DORA: Digital resilience in the financial sector

DORA, the Digital Operational Resilience Act, applies to financial entities and certain ICT third-party service providers. The regulation is designed to ensure that financial organisations remain operational even in the event of cyberattacks, IT outages or problems with service providers.

The focus is on ICT risk management, incident reporting, digital resilience testing, information sharing and third-party risk management. The handling of external ICT service providers is particularly important. Financial companies must know which providers are critical, what risks exist, which contractual requirements apply and which exit strategies are available.

DORA therefore makes it clear that digital resilience does not end at the company’s own boundaries. It also depends on how well suppliers, service providers and cloud providers are managed.

CRA: Cybersecurity for digital products

The Cyber Resilience Act takes a different approach. It focuses on products with digital elements, such as software, hardware, connected devices and digital components.

Manufacturers and providers must ensure that their products are securely developed, maintained and updated throughout their entire lifecycle. This includes secure development processes, vulnerability management, security updates, technical documentation and reporting obligations for actively exploited vulnerabilities.

As a result, cybersecurity moves deeper into product development, the software lifecycle, supply chains and product responsibility. Here, too, it is not enough to describe individual security measures. Companies need established processes, clear responsibilities and reliable documentation.

The common challenge: too many parallel compliance structures

Many companies respond to new regulation by launching new projects. This is understandable, but in the long term it creates a structural problem.

A separate risk register is created for NIS2. A separate service provider register is built for DORA. For the CRA, product development maintains its own lists of products, vulnerabilities and security updates. Data protection, information security, internal audit and business continuity teams also work with their own documentation.

On paper, this may initially look like progress. In reality, it creates a patchwork of disconnected structures.

The same risk appears multiple times but is assessed differently. A control is documented for several standards but is not maintained consistently. A measure is tracked in several lists without it being clear which status is actually up to date. A supplier is assessed from a data protection perspective but classified differently under DORA. A security incident is handled technically but not properly linked to regulatory reporting obligations.

The result is not more control. It is more complexity. And complexity is one of the biggest enemies of effective compliance.

The shared requirements of NIS2, DORA and CRA

Although the three regulations pursue different objectives, they overlap in several key areas. Companies should make use of these overlaps.

Risk management

All three regulations require companies to systematically identify, assess, treat and monitor risks. NIS2 mainly focuses on risks to network and information systems. DORA focuses on ICT risks and digital operational resilience. The CRA focuses on security risks related to digital products and their lifecycle.

The common denominator is clear: risks must not be viewed in isolation. A risk is almost always connected to systems, processes, suppliers, products, controls and measures. An integrated GRC approach makes these relationships visible.

Controls and measures

Regulatory requirements remain theoretical if they are not translated into concrete measures. Companies must be able to show which security measures have been implemented, who is responsible for them, when they were reviewed and whether they are effective.

Examples include access controls, backup concepts, incident processes, vulnerability management, supplier assessments, business continuity measures, security updates and awareness measures.

The decisive factor is not only that these measures exist. What matters is that they are up to date, traceable, assigned and auditable.

Incident management and reporting obligations

NIS2, DORA and the CRA all contain obligations for handling security incidents. Deadlines, formats and competent authorities may differ depending on the regulation. However, the operational need is very similar: companies must detect, assess, escalate, document and, where necessary, report incidents.

An isolated incident process is not enough. An incident must be linkable to affected systems, products, processes, customers, suppliers, risks and regulatory obligations. Only then can a company quickly decide whether reporting is required, which deadline applies and what information is needed.

Supplier and third-party risks

DORA places particular emphasis on third-party risks. But NIS2 and the CRA also increase pressure on supply chains, service providers and external technology partners.

Companies must know which suppliers are critical, what services they provide, which data or systems are affected, which security requirements apply and which contractual arrangements are in place. Without this transparency, blind spots quickly emerge, especially in relation to cloud services, software providers, managed services and critical ICT service providers.

Integrated vendor risk management is therefore becoming a key function of modern GRC programmes.

Evidence and audit readiness

Regulatory requirements are only truly fulfilled if companies can prove it. This is exactly where many compliance programmes struggle.

The individual policy is not the real problem. The challenge is proving that it has been implemented. The risk assessment alone is not enough. It must be linked to measures, responsibilities, status, reviews and decisions.

Audit readiness is created through consistent documentation. Companies need a central view of requirements, controls, risks, measures and evidence.

Why Excel and email are no longer enough

Many companies start their compliance work with spreadsheets, SharePoint folders, email coordination and PowerPoint reports. For individual tasks, this may work. But as soon as several regulations need to be managed at the same time, this approach quickly reaches its limits.

Excel can record risks, but it cannot manage reliable workflows. Email can distribute tasks, but it cannot ensure a dependable evidence chain. Folder structures can store documents, but they cannot map regulatory dependencies. PowerPoint can present management reports, but it cannot provide an up-to-date overall view.

The problem is not the individual tool. The problem is the missing connection between information.

A risk sits in one spreadsheet. The related measure sits in another. The evidence is stored in a folder. Responsibility was agreed by email. The supplier is assessed separately. The incident is handled in a ticketing system.

During an audit, an incident or a management discussion, all of this information has to be manually collected. This costs time, creates errors and makes decision-making harder.

What integrated GRC processes can deliver

An integrated GRC approach connects governance, risk management and compliance in one shared system. Instead of managing each regulation separately, requirements, risks, controls, measures and evidence are structured centrally.

The goal is not to artificially make NIS2, DORA and the CRA identical. The legal requirements remain different. The goal is to use shared processes intelligently.

For example, an access control may be relevant for ISO 27001, NIS2, DORA and internal security requirements. It should not be documented four times separately. It is much more effective to maintain this control centrally and map it to several requirements.

The same logic applies to risks, suppliers, incidents, policies, assets and measures. An integrated GRC system ensures that information is recorded properly once and then used multiple times.

The biggest benefit: Build once, use many times

The greatest value of integrated GRC processes lies in reusability. Companies do not need to create new structures for every regulation. Instead, they can assign existing content to multiple requirements in a targeted way.

A risk assessment, for example, may be relevant for NIS2, DORA, ISO 27001 and internal security objectives. An access security control may cover several regulatory requirements at the same time. A supplier can be assessed from the perspective of information security, data protection, business continuity and DORA. An incident can be analysed technically, classified from a regulatory perspective and documented organisationally. Evidence can be relevant not just for one audit, but for several reviews.

This is where efficiency is created. Effort decreases because information does not have to be recreated again and again. At the same time, quality improves because everyone works with the same data, assessments and evidence. Companies gain not only compliance, but also better control and governance.

What an integrated GRC system should be able to do

An integrated GRC system should be able to centrally map regulatory requirements from NIS2, DORA, the CRA and other standards. This also includes ISO 27001, GDPR, BSI IT-Grundschutz, ESG requirements and internal policies.

What matters is not just documentation. The decisive factor is connectivity: Which requirement applies to which area? Which control addresses it? Which risks exist? Which measures are in progress? Which evidence is available? Where are the gaps?

A central risk register creates transparency across information security risks, ICT risks, product security risks, supplier risks and operational risks. Risks should not only be described, but also assessed, assigned to responsible owners and linked to concrete measures.

Control management also plays a central role. Controls are the link between requirements and implementation. A good GRC system shows which controls exist, which requirements they are mapped to, when they were last reviewed and whether they are effective.

Structured measure management is equally important. Compliance often fails not because insights are missing, but because implementation is not tracked consistently. Clear tasks, responsibilities, deadlines, status information and escalation mechanisms are therefore essential.

Vendor risk management is particularly important. Suppliers and service providers must be assessed based on criticality, risk, data access, contractual requirements, security evidence and dependencies. Especially under DORA, NIS2 and the CRA, an isolated supplier register is not enough.

An integrated incident process also helps companies assess security incidents not only technically, but also from a regulatory and organisational perspective. Which systems are affected? Which processes are critical? Which customers or suppliers are involved? Are there reporting obligations? Which deadlines apply? Which evidence must be documented?

Finally, management also needs a clear view. NIS2, DORA and the CRA increase pressure on senior leadership. Risks, open measures, critical suppliers, compliance gaps, incident trends and audit status must therefore be presented in a clear and understandable way.

Integrated GRC processes improve more than compliance

Compliance is often seen as a box-ticking exercise. But NIS2, DORA and the CRA are not about paperwork. They are about real resilience.

A company is not more secure simply because it has many documents. It becomes more secure when it understands its risks, implements measures consistently, clarifies responsibilities, manages incidents effectively and learns from problems.

Integrated GRC processes support exactly that. They create transparency around dependencies, weaknesses, open measures and critical areas. They show where regulatory requirements and operational risks intersect.

This is particularly important because modern cyber risks rarely affect only one area. An attack can simultaneously involve IT, data protection, suppliers, business continuity, product responsibility and communication. Companies that manage these areas separately react more slowly. Companies that manage them in an integrated way identify connections earlier and can act more effectively.

Typical implementation mistakes

A common mistake is to view NIS2, DORA and the CRA purely as legal topics. Of course, they are legal requirements. But their implementation is operational. Companies need processes, responsibilities, controls and evidence.

A second mistake is assigning responsibility solely to IT. Cybersecurity is a technical topic, but not only a technical one. Procurement, product development, legal, compliance, data protection, risk management, audit and senior management all need to be involved.

Many companies also create separate control sets for every regulation. This quickly leads to duplication. A central control framework that maps requirements from several regulations is much more effective.

Suppliers are also often involved too late. Yet third-party risks are a central element of modern regulation. Companies that only assess suppliers shortly before an audit risk gaps in contracts, evidence, security requirements and exit strategies.

Another common weakness is evidence management. Audit readiness is not created on the day of the audit. It is created through continuous documentation. Evidence must be up to date, easy to find and linked to requirements.

How companies should approach this now

Companies should not begin by building three separate programmes for NIS2, DORA and the CRA. A shared foundation is the better approach.

The first step is to clarify which regulations are actually relevant. Then companies should review existing processes, controls, risks and evidence. In many organisations, a lot already exists, but it is distributed, inconsistently documented or difficult to find.

The next step is requirement mapping. Which obligations overlap? Which existing controls can be used? Which evidence is already available? Where are processes, responsibilities or documentation missing?

Based on this, companies can build an integrated GRC structure. This includes a shared risk register, a central control framework, structured measure management, integrated supplier management, a traceable incident process and clean evidence management.

The decisive success factor is consistency. Companies need a shared data basis, clear responsibilities and standardised workflows. Only then can regulatory requirements be fulfilled efficiently and managed sustainably.

The role of Zazoon GRC

Zazoon GRC helps companies manage regulatory requirements in an integrated rather than isolated way. Risks, controls, measures, evidence, audits, policies, suppliers and incidents can be managed centrally and connected with each other.

This allows companies to map requirements from NIS2, DORA, the CRA, ISO 27001, GDPR, BSI IT-Grundschutz and other frameworks in a structured way. Instead of maintaining parallel spreadsheets and manual evidence processes, companies create a transparent GRC foundation for compliance, risk management and cyber resilience.

This integrated approach is especially important for organisations that need to meet several regulatory requirements at the same time. It reduces effort, improves traceability and creates a clear foundation for audits, management decisions and continuous improvement.

Conclusion: The future of compliance is integrated

NIS2, DORA and the CRA show where European regulation is heading: away from isolated individual obligations and towards demonstrable resilience, clear responsibility and continuous risk management.

Companies that treat each regulation separately will struggle with growing complexity, duplicated effort and inconsistent evidence. Companies that build integrated GRC processes create a scalable foundation for current and future requirements.

The key point is this: NIS2, DORA and the CRA are not just compliance tasks. They are a wake-up call for better governance.

Companies that centrally connect risks, controls, measures, suppliers, incidents and evidence meet regulatory requirements more efficiently and make their organisation more resilient at the same time.

FAQ

What do NIS2, DORA and the CRA have in common?

NIS2, DORA and the CRA pursue different objectives, but they share many common requirements. All three regulations require structured risk management, clear responsibilities, security measures, documentation, incident processes and reliable evidence. This makes them well suited to being managed through integrated GRC processes.

Why should companies not implement NIS2, DORA and the CRA separately?

Separate implementation often leads to duplicated controls, parallel risk assessments, inconsistent evidence and high manual effort. An integrated approach reduces duplication and ensures that requirements, risks, controls and measures are centrally connected.

What is the difference between NIS2, DORA and the CRA?

NIS2 focuses on cybersecurity and risk management for many essential and important entities. DORA applies to the financial sector and focuses on digital operational resilience and ICT third-party risks. The CRA applies to products with digital elements and sets requirements for secure development, vulnerability management and product responsibility.

What role does GRC play in NIS2, DORA and the CRA?

GRC connects governance, risk management and compliance. For NIS2, DORA and the CRA, this means that requirements are managed centrally, risks are assessed, controls are mapped, measures are tracked and evidence is documented. This creates transparency around regulatory obligations and their operational implementation.

Which companies are affected by NIS2?

NIS2 applies to many companies in essential and important sectors, including energy, healthcare, transport, digital infrastructure, public administration, manufacturing, food, chemicals and digital services. Whether a company is affected depends, among other things, on its sector, size and national implementation.

Who is affected by DORA?

DORA applies to financial entities such as banks, insurers, payment institutions, investment firms and other financial market participants. It also affects certain ICT third-party service providers if they are critical to the financial sector.

Who is affected by the Cyber Resilience Act?

The Cyber Resilience Act applies to manufacturers, importers and providers of products with digital elements. This includes software, hardware, connected products and digital components. Companies must ensure that these products are securely developed, documented and maintained throughout their lifecycle.

Why is vendor risk management so important?

Many companies depend heavily on external service providers, cloud providers, software suppliers and ICT partners. NIS2, DORA and the CRA increase the pressure to make these dependencies transparent. Companies must know which suppliers are critical, what risks exist and which security requirements apply.

Is ISO 27001 enough to comply with NIS2, DORA or the CRA?

ISO 27001 is a very strong foundation for information security management, but it does not replace a regulation-specific assessment. Many controls and processes from ISO 27001 can be used for NIS2, DORA and the CRA. However, companies still need to assess which specific additional requirements apply.

How does Zazoon GRC support implementation?

Zazoon GRC helps companies centrally manage requirements, risks, controls, measures, evidence, audits, policies, suppliers and incidents. This allows multiple standards and regulations to be mapped in one integrated system. It reduces manual effort and improves transparency, audit readiness and governance.