Skip to content

15 September 2026 | 6 min

FINMA on Outsourcing: Why Externalisation Reduces Effort, but Not Responsibility

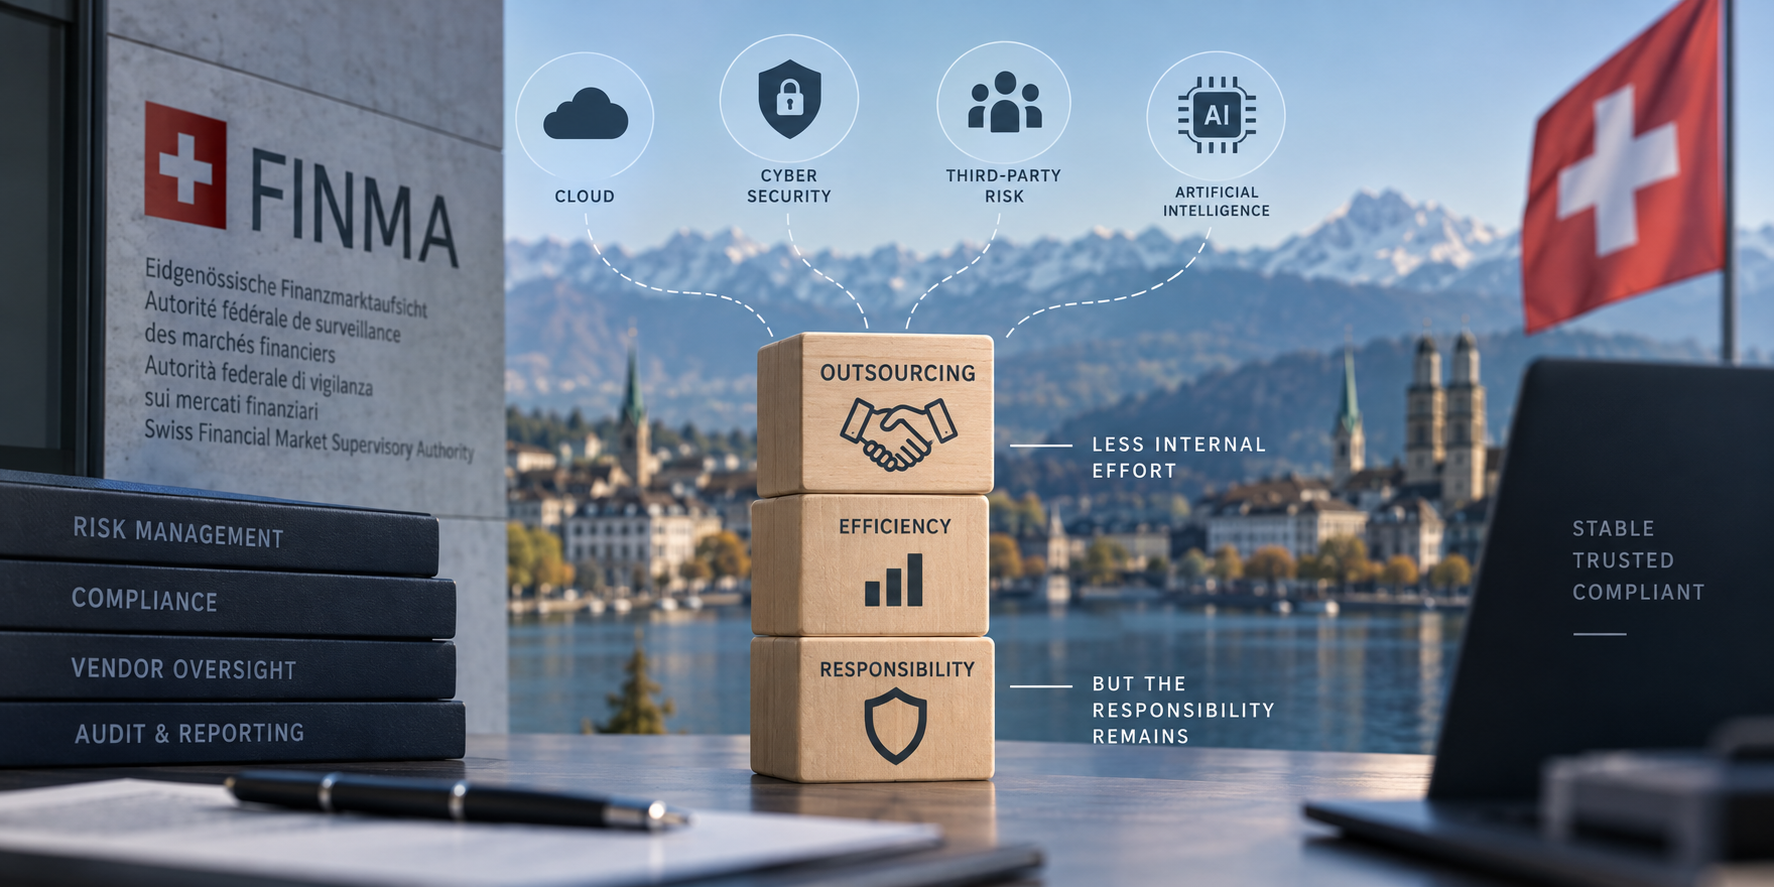
At the Small Banks Symposium on 7 September 2026, FINMA made an important point clear: proportionality does not mean that material risks can be taken less seriously. Especially when it comes to cyber risks, outsourcing, cloud providers and artificial intelligence, responsibility remains with the supervised institution.

Smaller banks can benefit significantly from sourcing technology or services externally. They do not need to build the same internal structures as large institutions. But they still need to know and effectively manage their material risks. This is exactly where outsourcing becomes a GRC topic.

FINMA emphasises that smaller institutions can benefit from proportionate supervision. At the same time, outsourcing may reduce internal effort, but it does not reduce responsibility for risk management, controls and evidence.

Cyber risks, cloud dependencies, concentration risks and the use of AI are particularly in focus. External providers can make processes more efficient, but they also create new dependencies.

For financial institutions, this means that outsourcing must not only be regulated contractually. It needs to be managed as an ongoing governance process. This includes risk analysis, responsibilities, controls, vendor oversight, exit planning and audit-ready evidence.

Proportionality Does Not Remove Responsibility

Proportionality is important for smaller banks and financial institutions. Requirements should be implemented in a way that reflects size, complexity, business model and risk profile. This is reasonable, because smaller institutions do not have the same resources as large banks.

However, FINMA makes clear that proportionality does not mean that key risks can be ignored or weakly managed. For topics such as money laundering, sanctions, cyber risks or outsourcing, the size of the institution can only be a limited argument for reduced expectations.

The decisive point is responsibility. A financial institution can outsource an IT service, a cloud platform, an operational function or a security capability. But responsibility towards customers, supervisors and management remains internal.

Why Outsourcing Is Becoming More Critical in Finance

Outsourcing has long been part of everyday operations in financial institutions. IT operations, cloud infrastructure, payment processes, core banking systems, data analytics, cybersecurity, customer communication and compliance-related services are increasingly provided by external vendors.

This creates clear benefits. Institutions can access specialist expertise, reduce costs, gain scalability and adopt modern technologies faster. Smaller banks in particular benefit because they do not need to build complex capabilities fully in-house.

At the same time, new risks emerge. When important processes are handled by external providers, dependencies arise. When many institutions use the same cloud or technology providers, concentration risks increase. When vendors provide AI systems, data platforms or security services, oversight becomes more complex.

Outsourcing is therefore not merely a procurement or IT topic. It is a governance topic.

Cloud and Technology Providers: Efficiency Meets Concentration Risk

The increasing use of cloud and technology providers is a double-edged issue for financial institutions. On the one hand, it enables modern, secure and scalable infrastructure. On the other hand, it can create strong dependencies on a small number of large providers.

For GRC leaders, the key task is to make these dependencies visible. Which critical processes run with which provider? Which data is processed? Which subcontractors are involved? Which outage or security risks exist? How quickly could the institution react if a provider failed or suffered a serious security incident?

FINMA’s perspective is clear: smaller institutions may use pragmatic solutions. But they must know and effectively manage their material risks. This requires structured third-party risk management.

AI Changes Both Sides of the Risk

FINMA’s reference to artificial intelligence is particularly interesting. AI can support financial institutions, for example in process automation, fraud detection, customer service, risk analysis or cybersecurity. At the same time, AI can make attacks easier to automate and scale.

This changes both the opportunity side and the threat landscape. An institution may use AI functionality from an external provider without fully understanding the underlying models, data flows or security mechanisms. At the same time, attackers can use AI to make phishing, social engineering, malware or fraud attempts more professional.

For outsourcing, this means that vendor assessments will increasingly need to consider AI governance, data processing, model risks, security controls and transparency. This is especially important where AI is used in critical processes or customer-relevant decisions.

What a Good Outsourcing Framework Needs to Do

An effective outsourcing framework does not start with the contract. It starts with the question of which processes are critical and which risks arise from outsourcing them. Providers then need to be assessed, controls defined and responsibilities clarified.

Ongoing monitoring is equally important. A provider that is acceptable today may have a different risk profile tomorrow because of new subcontractors, changed services, security incidents or regulatory expectations. Outsourcing risks are dynamic.

Financial institutions should therefore not only maintain a list of vendors. They need a central view of criticality, contracts, controls, risk acceptances, findings, actions, dependencies and exit scenarios.

Conclusion: Outsourcing Needs Internal Control

FINMA makes clear that outsourcing can be useful and efficient for smaller banks. But it does not transfer responsibility to the service provider. Cyber risks, cloud dependencies, concentration risks and AI use must be understood and managed internally.

For GRC leaders, the message is clear: outsourcing requires transparency. Which providers are critical? Which risks exist? Which controls are in place? Which evidence is available? And how quickly can the institution react if a provider fails or suffers a security incident?

Zazoon supports financial institutions in centrally managing outsourcing, vendor risk, cyber risks, controls and evidence. This turns outsourcing from a blind spot into a controlled component of modern governance.

FAQ

What did FINMA say about outsourcing?

FINMA emphasises that smaller institutions can outsource technology and services, but responsibility for appropriate risk management remains with the supervised institution.

Why is outsourcing a GRC topic?

Outsourcing connects vendor risk, cybersecurity, operational resilience, compliance, internal controls, audit and management responsibility. It is not only about contracts, but about ongoing oversight.

Which risks are most relevant?

Cyber risks, cloud dependencies, concentration risks, subcontractors, data risks, outage risks and new risks from AI use are particularly relevant.

What does proportionality mean?

Proportionality means that requirements can be implemented in a way that reflects size, complexity and risk profile. It does not mean that material risks can be taken less seriously.

What should financial institutions review now?

Institutions should review their critical service providers, cloud dependencies, subcontractors, controls, exit scenarios, risk acceptances and evidence in a structured way.

How does Zazoon help?

Zazoon helps connect service providers, risks, controls, responsibilities, assessments, findings and evidence in one central GRC system. This makes outsourcing manageable, traceable and audit-ready.

Related posts

21 August 2026 | 9 min

EU Retail Investment Strategy: Why “Value for Money” Is Becoming the New GRC Benchmark in Financial Distribution

The EU Retail Investment Strategy aims to strengthen the European market for retail investments while improving investor protection. At the centre of the reform is a concept that will become highly relevant for banks, insurers, asset managers, wealth managers and financial distributors: “Value for Money”.

The message is clear: in future, financial institutions will not only need to disclose costs, risks and product characteristics correctly. They will increasingly need to demonstrate that a product provides fair value for its intended target market.

This shifts the regulatory focus. Product documentation becomes product governance. Cost transparency becomes evidence. Distribution control becomes a GRC topic that connects requirements, target markets, costs, client outcomes, remuneration, marketing and audit trails.

The EU Retail Investment Strategy reforms key rules for financial distribution, including areas linked to MiFID II, IDD, PRIIPs, UCITS and AIFMD. Its objective is to improve investor protection, make access to capital markets easier and increase trust in financial products.

The main GRC driver is “Value for Money”. Financial products should not only be transparent. They should provide a demonstrable and reasonable balance between costs, fees, risks, performance potential and client benefit.

For financial institutions, this means stronger requirements for product approvals, target market definitions, cost and fee analysis, suitability processes, inducements, marketing controls and evidence management.

Swiss institutions may also be indirectly affected, particularly through EU subsidiaries, EU branches, cross-border distribution or EU distribution partners.

Why “Value for Money” Marks a Shift

Financial distribution regulation has long focused on transparency. Clients should understand what a product costs, which risks it carries and what characteristics it has. That remains important, but it is no longer enough.

Value for Money goes further. The question is no longer only whether everything has been disclosed. The question is whether the product is appropriate for the target market when costs, services, performance potential, risk and distribution model are considered together.

This is a shift from formal compliance to outcome-oriented governance. A product can be correctly documented and still become problematic if costs and fees are not proportionate to the expected client benefit.

For GRC leaders, this is the key point. Value for Money does not create a single new checklist. It requires existing processes to be connected. Product development, product approval, target market assessment, cost analysis, distribution, advice, marketing and ongoing monitoring must work together.

Product Governance Becomes More Evidence-Based

Financial products are often created and distributed through complex structures. Asset managers, issuers, banks, platforms, insurers and distributors may all have different roles. The Retail Investment Strategy increases the pressure to document these roles more clearly.

Product manufacturers must be able to explain why a product is suitable for the defined target market. This includes a clear assessment of costs and fees. Distributors, in turn, must ensure that they recommend or offer products only to clients for whom they are appropriate.

This makes product governance more operational. Institutions must not only have a product approval process. They must be able to show which criteria were reviewed, which data was used, what trade-offs were considered and who approved the decision.

For compliance and internal audit teams, this is crucial. The audit question will not only be whether a process exists. It will be whether the process leads to appropriate decisions and whether those decisions are documented in a defensible way.

Costs, Fees and Client Benefit Move Closer Together

Value for Money turns costs and fees into a central governance data point. Institutions must not only disclose costs, but place them in the context of client value. Peer group comparisons, benchmarks, cost structures, expected returns, risk-return profiles and target market assumptions may all become relevant.

This is challenging because many data sources are involved. Product data, cost information, performance data, risk metrics, target market information, remuneration structures and distribution data often sit in different systems. If these data points are inconsistent, evidence gaps emerge.

A product may be considered appropriate during product approval, while distribution materials later use outdated cost information. Or a product may be approved for a defined target market but marketed too broadly through digital channels. These inconsistencies are exactly where GRC risks arise.

Inducements Remain a Control Topic

Inducements are one of the most sensitive issues in the Retail Investment Strategy. The political debate around a full ban has been intense. The current direction is more focused on stronger controls, better transparency and evidence that client interests are protected.

For institutions, this means that remuneration models must be connected more closely with product governance and distribution controls. It must be clear which incentives exist, how conflicts of interest are identified and which controls prevent remuneration from improperly influencing product selection or advice.

Inducements are therefore not only a legal or disclosure topic. They become part of the internal control system. Institutions must be able to show that remuneration, product approvals, client interests and advisory obligations are assessed together.

Suitability and Distribution: From Client Profile to Evidence Chain

Suitability processes will also become more important. In investment advice and distribution, institutions must be able to demonstrate that a product fits the client’s knowledge, experience, risk tolerance, investment objectives and ability to bear losses.

The GRC issue lies in the evidence chain. A single advisory form is not enough if the underlying product data, target market definition, cost information and distribution rules are not aligned. Institutions must ensure that recommendations result from a consistent process.

This is particularly relevant for digital distribution channels. Robo-advice, online platforms, app-based investment offerings and automated product recommendations generate large volumes of data and decisions. These need to remain controlled, versioned and auditable.

Marketing Becomes Part of Product Governance

Marketing in financial distribution is not just communication. Product descriptions, performance statements, ESG references, cost information, risk warnings and digital campaigns influence how clients understand a product.

Value for Money strengthens this connection. If a product is promoted with certain benefits, the marketing message must align with product governance, target market definition and the cost-benefit assessment. Marketing claims cannot be created in isolation.

For GRC teams, this creates a clear need for approval and control processes. Product information, campaigns, websites, factsheets and digital distribution materials should be reviewed and versioned in a traceable way. This becomes even more important in cross-border distribution, where requirements and supervisory expectations may differ by market.

Why Swiss Institutions Should Pay Attention

The Retail Investment Strategy is EU regulation. Swiss financial institutions are therefore not automatically directly affected. However, the topic is relevant for many Swiss providers.

This applies especially where an institution has EU subsidiaries, EU branches, EU distribution partners or cross-border business with EU clients. Even if a Swiss institution is not directly addressed, EU partners may request additional evidence.

In practice, this may mean that Swiss asset managers, wealth managers or product providers need to document more clearly how costs, target markets, product benefits, risks and distribution information fit together. EU distribution partners will need this information to meet their own obligations.

This creates an indirect GRC effect across the distribution chain.

What Financial Institutions Should Do Now

Institutions should first assess whether their product governance is ready for Value for Money. This is not only about product approvals. It is about whether costs, target markets, client benefit, risk, remuneration and distribution are assessed and documented consistently.

They should then review which data sources are used for costs, performance, risk, target market and distribution. If this data is not current, consistent or centrally available, implementation risk increases.

A review of distribution channels is also important. Personal advice, digital platforms, insurance distribution, cross-border distribution and partner distribution all create different control points. Value for Money must work across all relevant channels.

Finally, institutions should define the audit trail early. Trying to reconstruct decisions later creates unnecessary effort and risk.

Conclusion: Value for Money Makes Financial Distribution More Auditable

The EU Retail Investment Strategy shows where financial regulation is heading. Transparency remains important, but it is not enough. Products for retail clients should not only be understandable. They should provide demonstrable value.

For GRC leaders, the direction is clear: product governance is becoming more outcome-oriented and more evidence-based. Institutions need to connect costs, target markets, client benefit, remuneration, distribution and controls more closely.

Those that build structured processes, clear responsibilities and audit-ready evidence early will reduce regulatory risk and strengthen trust with clients, supervisors and distribution partners.

Zazoon supports financial institutions in managing Value for Money as an integrated GRC process: from requirements and product governance to risks, controls, evidence, findings and management reporting.

FAQ

What is the EU Retail Investment Strategy?

The EU Retail Investment Strategy is a reform package designed to strengthen the retail investment market in Europe. It aims to improve investor protection, enhance product information and make access to capital markets easier.

What does “Value for Money” mean?

Value for Money means that financial products should provide appropriate value for the intended target market. Costs, fees, risks, services and client benefit must be aligned in a demonstrable way.

Which financial institutions are affected?

The topic is particularly relevant for banks, investment firms, asset managers, insurers, insurance distributors and other financial service providers with EU exposure.

Why is Value for Money a GRC topic?

Because it connects product governance, cost analysis, target market definition, suitability, inducements, marketing controls and evidence. It is not only about disclosure, but about auditable decision-making.

Are Swiss institutions affected?

Not automatically. However, Swiss institutions may be indirectly affected if they have EU subsidiaries, EU branches, EU distribution partners or cross-border business with EU relevance.

What should institutions do now?

They should review their product governance, cost and fee processes, target market definitions, distribution controls, inducement controls and audit trails for Value for Money readiness.

How does Zazoon help?

Zazoon helps connect requirements, products, target markets, risks, controls, approvals, actions and evidence in one central GRC system. This makes Value for Money traceable, manageable and audit-ready.

14 July 2026 | 9 min

FINMA Quantum Computing: Why Post-Quantum Cryptography Is Becoming a GRC Issue

On 9 July 2026, FINMA published Supervisory Communication 05/2026 on quantum computing. This is not a research paper or a distant future scenario. It is a clear message to all supervised Swiss financial institutions: the time for simply observing developments is over. Organisations that do not start preparing a strategy for quantum-safe encryption today risk facing a compliance problem tomorrow.

FINMA based its assessment on a survey conducted between November 2025 and January 2026 among 60 banks, insurance companies, asset managers and financial market infrastructures. The results are sobering: the risks are widely recognised, but concrete measures are still missing in most organisations.

This article looks at what FINMA found, what it now expects from supervised institutions and how governance structures and GRC software can support the transition to post-quantum cryptography.

FINMA published its Guidance 05/2026 on quantum computing in July 2026 and expects supervised institutions to actively integrate the topic into their risk management.

According to the survey, 72 percent of respondents have not yet planned or implemented measures for quantum-safe encryption, while only 8 percent have a concrete migration plan. Around two thirds expect that a sufficiently powerful quantum computer could become capable of breaking common RSA-2048 encryption within ten years.

One of the most immediate concerns is the so-called “harvest now, decrypt later” scenario, in which encrypted data is intercepted today and stored until future quantum computers are able to decrypt it.

FINMA recommends action in five areas: strategy and roadmap, risk analysis and inventory, protection of critical data, crypto-agility and management of external service providers. A concrete PQC migration plan should be in place by mid-2027.

Why Quantum Computing Is Already a Compliance Topic

Quantum computers do not yet exist at a scale that threatens today’s commonly used encryption methods. That is true, but it is also a dangerous reason to delay action.

Many widely used public-key cryptographic methods, including RSA, ECDSA and EC-DH, rely on mathematical problems that are extremely difficult for classical computers to solve. A sufficiently powerful quantum computer could fundamentally change this.

The real challenge is that a migration to quantum-safe encryption will take years. It affects ICT systems, applications, infrastructure, digital signatures, authentication mechanisms and external interfaces. Organisations that wait until cryptographically relevant quantum computers are available may simply have too little time left to migrate safely.

There is also the “harvest now, decrypt later” risk. Attackers can intercept encrypted data today and store it with the intention of decrypting it in the future. Long-lived sensitive information such as customer data, contracts, transaction histories or identity information may therefore already be exposed to a future risk.

What the FINMA Survey Shows: Awareness Without Action

The survey results reveal a clear gap between risk awareness and operational readiness.

72 percent of the surveyed institutions have not yet planned or implemented any measures for the transition to quantum-safe encryption. 28 percent have at least made a strategic decision at executive management or board level, and 20 percent have an active project underway.

However, only 8 percent currently have a concrete migration plan with target dates. Those organisations generally expect a complete migration to take around four to five years.

At the same time, 43 percent of respondents have not yet made any decision on a future migration plan. FINMA therefore sees a growing need for action, especially given ongoing technological progress, long migration timelines and uncertainty around when cryptographically relevant quantum computers will become available.

The surveyed institutions also see opportunities in quantum computing, particularly in areas such as risk and portfolio analysis, transaction monitoring and algorithmic trading. However, almost two thirds expect that they will only use quantum computing applications themselves in eight years or more.

What FINMA Recommends: Five Priority Areas

FINMA Guidance 05/2026 outlines five areas that supervised institutions should integrate into their internal risk management.

Strategy and Roadmap

FINMA expects institutions to develop a board-supported strategy for the transition to quantum-safe encryption. This should be translated into a concrete implementation plan with milestones and target dates for the overall migration as well as for particularly critical business processes and data.

A PQC migration plan should be available by mid-2027 at the latest. It can form part of an existing cybersecurity strategy, but it should contain clear and specific objectives for the post-quantum transition.

Risk Analysis and Cryptographic Inventory

Before migrating anything, organisations need a clear picture of their current environment.

FINMA recommends analysing business processes and identifying all encryption, signature and authentication methods currently in use. The result should be a comprehensive cryptographic inventory covering ICT systems, applications, infrastructure and external interfaces, regardless of whether they are operated internally, outsourced or consumed as a service.

This inventory should make it possible to identify which algorithms are vulnerable to quantum attacks and where migration is required. It also needs to be kept continuously up to date.

Protection of Critical Data

FINMA recommends paying particular attention to information that requires long-term protection.

The “harvest now, decrypt later” risk should explicitly be included in risk assessments. Data that must remain confidential for ten, twenty or more years should be prioritised when preparing for post-quantum cryptography.

Because there is still limited long-term operational experience with PQC algorithms, many organisations are considering hybrid approaches that combine classical cryptography with post-quantum algorithms during the transition period.

Crypto-Agility

Crypto-agility is the ability of an ICT system to replace cryptographic algorithms quickly and flexibly without requiring major changes to the underlying software architecture.

FINMA recommends including crypto-agility as a requirement in new ICT developments and procurement processes.

The goal is straightforward: if an algorithm becomes insecure or a new standard is introduced, organisations should be able to switch without triggering another multi-year migration project. Crypto-agility is therefore not only a technical capability, but also a governance principle for resilient IT infrastructures.

External Service Providers

Outsourcing does not remove responsibility from the supervised institution. This also applies to the transition to post-quantum cryptography.

If an external provider operates systems, applications or infrastructure for a financial institution, that provider will also need to support the transition to quantum-safe cryptography.

FINMA therefore recommends including crypto-agility and future cryptographic requirements in new outsourcing agreements for software and data services and addressing existing contracts as early as possible.

What This Means for Compliance and Risk Teams

FINMA Guidance 05/2026 is not a new standalone legal obligation in the narrow sense. However, it makes clear that existing technology-neutral requirements for governance and risk management also apply to quantum risks.

For compliance and risk teams, this means quantum risks should become part of the existing cyber and operational risk framework rather than being managed in isolation.

Third parties and software suppliers also need to be included early in the planning process. The survey indicates that many institutions have already started contacting software providers or intend to do so, which reflects the strong dependency on external technology partners.

Another important point is timing. Governance preparation can and should move faster than the technical migration itself. A board decision, a strategy, a risk assessment and a cryptographic inventory can be established relatively quickly, while the technical transition may take several years.

GRC Software as the Structural Foundation for PQC Migration

All five FINMA recommendations have one thing in common: they depend on structured, documented and continuously maintained processes.

A cryptographic inventory covering systems, applications and external interfaces becomes difficult to manage without a central system. The same applies to quantum risk assessments, migration plans, responsibilities, milestones and evidence for supervisory reviews.

GRC software provides a structured foundation for this work. It can help integrate quantum risks into the existing risk management framework, connect relevant assets and third parties, assign responsibilities, document migration measures and provide management visibility into progress.

PQC should also not be treated as an isolated project. It forms part of a broader cyber risk environment that can overlap with other regulatory and governance requirements. Managing these topics in one integrated GRC environment can reduce duplication and prevent the creation of parallel documentation structures.

Zazoon: GRC Software for Tomorrow’s Requirements

At Zazoon, we have developed GRC software to translate complex regulatory requirements into structured and manageable processes.

For financial institutions preparing to implement FINMA’s quantum computing guidance, this means there is no need to create another isolated project silo. PQC requirements can instead be integrated into the existing risk management and governance environment.

Quantum risks, responsibilities, third-party dependencies, measures and supporting evidence can be managed centrally and made transparent for management, audit and supervisory discussions.

Conclusion: It Is Not About If, but When

Cryptographically relevant quantum computers do not yet exist. But the transition to quantum-safe encryption is a multi-year undertaking, and FINMA has made clear that preparation should begin now.

Institutions that do not have a PQC migration plan by mid-2027 may face increasing regulatory and technical pressure as migration windows become narrower.

The first step does not need to be a massive technical programme. It starts with governance: strategy, inventory, risk analysis and third-party requirements.

This is exactly where GRC software can provide the greatest value. Organisations that establish the right structures today will be better prepared for the cryptographic transition of tomorrow.

FAQ

What does FINMA require regarding quantum computing?

FINMA expects supervised financial institutions to actively integrate quantum risks into their existing risk and governance frameworks. This includes a clear strategy, a cryptographic inventory, risk assessments, the protection of particularly sensitive data, crypto-agility and the involvement of external service providers.

By when should a PQC migration plan be in place?

FINMA recommends developing a concrete migration plan for Post-Quantum Cryptography by mid-2027 at the latest. The plan should include target dates, milestones and priorities for critical systems, processes and data.

What does “Harvest now, decrypt later” mean?

This attack scenario involves encrypted data being intercepted and stored today so that it can potentially be decrypted once sufficiently powerful quantum computers become available. Data that needs to remain confidential for many years is therefore particularly at risk.

What is crypto-agility?

Crypto-agility describes the ability of IT systems to replace cryptographic methods flexibly and with minimal effort. This allows organisations to react more quickly when existing algorithms become insecure or new standards need to be introduced.

Why are external service providers important for PQC migration?

Many financial institutions rely on external providers for software, infrastructure and data services. However, responsibility for outsourced functions remains with the supervised institution. Suppliers and outsourcing partners therefore also need to be included in the PQC strategy and in requirements for crypto-agility.

What role does GRC software play in preparing for Post-Quantum Cryptography?

GRC software can help organisations centrally manage quantum risks, cryptographic dependencies, third parties, responsibilities and migration measures. This makes it easier to document progress, risks and evidence in a structured way and provide transparency for management, auditors and regulators.

16 June 2026 | 12 min

Cyber Europe 2026: Why Cyber Resilience Is Becoming a Management Priority

Cyber Europe 2026 was the eighth major European cyber crisis exercise organised by the European Union Agency for Cybersecurity, ENISA. The exercise took place on 10 and 11 June 2026 and tested how well Europe can respond in a coordinated way to large-scale cyber incidents.

The focus was on the railway and maritime sectors. The exercise simulated the handling of parallel cyber incidents affecting critical transport and logistics infrastructure. It was not only about technical defence, but also about crisis coordination, business continuity, communication with authorities, situational awareness, decision-making processes and the continuity of essential services.

Participants included European authorities, national cybersecurity bodies, operators of critical infrastructure and other organisations from the European cyber ecosystem. Switzerland also took part. Under the lead of the Federal Office for Cybersecurity, BACS, various national and cantonal authorities as well as operators of critical infrastructure participated in the exercise.

For companies, Cyber Europe 2026 sends an important signal: cyber resilience is no longer measured only by the existence of security policies. What matters is whether organisations can remain operational during an incident, make clear decisions, coordinate their response and document their actions in a reliable way.

Cyber Europe 2026 was a Europe-wide cyber crisis exercise organised by ENISA, with a focus on railway and maritime transport.

The exercise tested responses to parallel cyber incidents, coordination between authorities and operators, and the ability to maintain essential services.

Switzerland participated under the lead of BACS. National and cantonal authorities as well as operators of critical infrastructure were involved.

For companies, the exercise shows that cyber resilience goes far beyond IT security. Incident response, business continuity management, crisis communication, vendor management and management responsibility must work together.

In the context of NIS2, critical infrastructure and rising cyber risks, operational evidence is becoming increasingly important. Companies must not only plan, but also exercise, document and improve.

What Is Cyber Europe 2026?

Cyber Europe is a regular European cyber crisis exercise organised by ENISA. It brings together authorities, critical sectors and cybersecurity organisations. The goal is to simulate realistic cyber crises and test how well collaboration, escalation and crisis response work in practice.

Cyber Europe 2026 focused on transport networks, especially rail and maritime infrastructure. Both sectors are highly connected, internationally dependent and essential for the economy, supply chains and mobility. A cyberattack on such infrastructure can have consequences far beyond a single company.

For this reason, the exercise was not designed as an isolated technical test. It aimed to show how organisations work together under pressure, exchange information, make decisions and keep operations as stable as possible.

What Was Tested During Cyber Europe 2026?

The exercise centred on several parallel cyber incidents. Such scenarios are particularly demanding because they put organisations under pressure at the technical, operational and strategic levels at the same time.

The exercise tested, among other things, how quickly incidents are detected and assessed, how information flows between the parties involved, how crisis teams make decisions and how essential services can be maintained despite cyberattacks.

Business continuity was also a key element. A cyber incident is not just an IT problem when timetables, logistics processes, port operations, communication systems or safety-related operational processes are affected. Companies need to know which processes are critical, which dependencies exist and which alternatives are available in an emergency.

Another focus was coordination. Cyber crises can quickly cross organisational and national boundaries. Operators, service providers, authorities, regulators, crisis teams and communication teams must work together under time pressure. In real crises, these interfaces are often the biggest weakness.

Why the Railway and Maritime Sectors Were in Focus

Railway and maritime transport are central components of European mobility and supply chains. They connect passenger transport, goods flows, ports, industry, energy supply and international trade routes.

At the same time, these sectors are becoming increasingly digital. Operational control systems, communication networks, booking platforms, port management, logistics data, sensors and automated processes increase efficiency, but also create new attack surfaces.

A successful cyberattack can therefore have far-reaching consequences. It can delay supply chains, disrupt passenger transport, increase safety risks and damage public trust.

Cyber Europe 2026 therefore illustrates a challenge that applies to many critical sectors: the more connected organisations become, the more important robust cyber resilience, clear responsibilities and tested crisis processes become.

Why Switzerland’s Participation Matters

Switzerland participated in Cyber Europe 2026 and tested its cyber resilience in the railway and maritime sectors. The exercise was led in Switzerland by the Federal Office for Cybersecurity, BACS. National and cantonal authorities as well as operators of critical infrastructure were involved.

This is relevant for two reasons. First, cyber risks are cross-border by nature. Even though Switzerland is not a member of the EU, it is closely connected to European transport, energy, financial and supply chains. An incident in a neighbouring country can affect Swiss organisations, and vice versa.

Second, Switzerland’s participation shows that cyber resilience is not only a matter for national authorities. It is created through cooperation between the state, the private sector, critical operators and specialised service providers. In major incidents, it matters whether this cooperation has already been tested.

For Swiss companies, the message is clear: cyber crises must not only be prepared for technically. They require crisis leadership, reporting channels, roles, supplier contacts, recovery plans and documented decision-making processes.

Cyber Europe 2026 and NIS2: What Companies Should Take Away

Cyber Europe 2026 fits directly into current developments around NIS2. The directive strengthens requirements for cybersecurity, risk management, incident reporting and management responsibility in important and essential entities.

The exercise shows what matters in practice. Companies must not only meet requirements, but also demonstrate that their processes work during an actual incident. This is especially relevant for incident response, business continuity management, crisis communication and the management of external dependencies.

NIS2 is becoming increasingly operational. A policy alone is not enough. A company must know who makes decisions during an incident, which systems are critical, which service providers need to be involved, which reporting deadlines apply and which evidence must be available afterwards.

Cyber Europe 2026 makes one thing clear: cybersecurity readiness must be exercised. Only then can companies see whether roles are clear, escalation paths work and measures are effective in practice.

Why Cyber Resilience Is More Than IT Security

Cyber resilience describes an organisation’s ability to prevent, detect, manage and recover from cyber incidents. This goes far beyond traditional IT security.

Technical protection measures remain important. But during a crisis, organisational factors are just as decisive. These include clear responsibilities, fast decision-making, crisis communication, emergency processes, supplier coordination and the ability to continue critical business processes.

A company can be technically well positioned and still fail during a crisis if it is unclear who decides, who communicates or which systems need to be restored first.

Conversely, an organisation with strong governance can respond faster, limit damage and learn from incidents. Cyber resilience is therefore a management topic and a central part of modern GRC structures.

The Role of Business Continuity Management

Business continuity management, or BCM, plays a central role in cyber crises. It answers the question of how critical processes can continue when systems, service providers or locations fail.

Cyber Europe 2026 shows that BCM should not be viewed separately from cybersecurity. A cyber incident can disrupt business processes just as severely as a natural disaster, power outage or supply chain disruption.

Companies should therefore review whether their BCM plans are realistic from a cyber perspective. Are recovery priorities defined? Are critical processes known? Are dependencies on service providers documented? Are alternative communication channels available? Have crisis roles been tested?

BCM proves its value not on paper, but in exercises. Companies that regularly simulate cyber crises identify weaknesses before a real incident exposes them.

Incident Response: From Plan to Tested Reaction

Many companies have incident response plans. The decisive question is whether these plans work under pressure.

Cyber Europe 2026 shows that incident response is dynamic. Information is incomplete, decisions must be made quickly and multiple stakeholders are involved at the same time. This is why a static process document is not enough.

Effective incident response requires clear roles, defined escalation levels, communication rules, technical analysis capabilities and links to management, legal, data protection, communications and business departments.

Post-incident review is just as important. Every incident and every exercise should be documented and evaluated. Which decisions were made? Which measures worked? Where were there delays? Which controls need to be improved?

This turns incident response into a continuous improvement process.

Suppliers and External Dependencies as a Risk Factor

Cyber crises rarely affect only one organisation. Many critical processes depend on IT service providers, cloud providers, software vendors, network operators, logistics partners or specialised platforms.

Such dependencies are particularly important in the railway and maritime sectors. But the same principle applies in other industries: companies that do not know their critical third parties will struggle to respond quickly and effectively during an incident.

Companies should therefore know which service providers are relevant for critical processes, which contact and escalation channels exist, which contractual obligations apply and which evidence is available.

Vendor risk management is becoming a permanent part of cyber resilience. It is not enough to assess suppliers once. Dependencies must be monitored continuously and included in crisis exercises.

Why Evidence and Documentation Are Critical

After a cyber crisis, it is not only important what was done. It is also important whether the company can show what was done in a reliable and traceable way.

Documentation is therefore not an administrative side issue. It is central for audits, regulatory inquiries, internal lessons learned, insurance claims, customer communication and possible legal assessments.

In an emergency, companies must be able to trace when an incident was detected, who was informed, which decisions were made, which measures were implemented and which systems were affected.

Cyber Europe 2026 shows that evidence is part of resilience. Companies that cannot document their response will later struggle to demonstrate effectiveness, due care and improvement.

What Companies Should Do Now

Companies should use Cyber Europe 2026 as an opportunity to review their own crisis readiness. The most important step is an honest assessment of the current state.

Are critical processes known? Are incident response plans up to date? Are roles and escalation paths clear? Have crisis exercises been conducted? Are suppliers integrated into emergency processes? Is there a connection between cybersecurity, BCM, risk management and management reporting?

Tabletop exercises are particularly useful. They allow organisations to run through a realistic crisis scenario without affecting production systems. Such exercises quickly show whether responsibilities are clear and whether decision-making paths work.

Companies should also review their evidence management. Risks, controls, measures, incidents, exercises and lessons learned should not be scattered across individual files, but managed in a structured way.

Common Weaknesses in Cyber Crises

Many organisations underestimate organisational weaknesses. In practice, crisis response rarely fails only because of missing technology. More often, the problem lies in unclear responsibilities, outdated contact lists, slow escalation, incomplete situational awareness or inconsistent communication.

Another weakness is the separation of IT and business processes. If technical teams do not know which processes are business-critical, recovery priorities may be set incorrectly.

External dependencies are also often considered too late. If a critical service provider cannot be reached or contractual reporting channels are unclear, the company loses valuable time.

Cyber Europe 2026 therefore shows that resilience is not created by individual measures. It is created through the interaction of people, processes, technology, governance and practice.

Conclusion

Cyber Europe 2026 was an important practical test of Europe’s cyber resilience. The focus was on railway and maritime transport, two sectors whose disruption can have far-reaching consequences for mobility, supply chains and public safety.

The exercise clearly shows that cybersecurity is no longer a purely technical task. Companies must be able to manage cyber incidents organisationally, operationally and strategically. This includes incident response, business continuity management, crisis communication, vendor management, management responsibility and reliable evidence.

For companies in Europe and Switzerland, the most important lesson is this: cyber resilience must be exercised. Plans, policies and controls are necessary, but only realistic exercises show whether they work in practice.

Cyber Europe 2026 is not just an isolated public-sector event. It is a clear signal to all organisations: the next stage of cybersecurity is operational resilience.

FAQ on Cyber Europe 2026

What is Cyber Europe 2026?

Cyber Europe 2026 was a Europe-wide cyber crisis exercise organised by ENISA. Its goal was to test Europe’s collective response capability during major cyber incidents and strengthen the cyber resilience of essential services.

When did Cyber Europe 2026 take place?

Cyber Europe 2026 took place on 10 and 11 June 2026.

Which sectors were in focus?

The exercise focused on the railway and maritime sectors. It tested the handling of cyber incidents that could affect transport and logistics infrastructure.

Did Switzerland participate in Cyber Europe 2026?

Yes. Switzerland participated under the lead of the Federal Office for Cybersecurity, BACS. National and cantonal authorities as well as operators of critical infrastructure were involved.

What was tested during Cyber Europe 2026?

The exercise tested incident response, crisis coordination, business continuity, information exchange, communication with authorities and the ability to maintain essential services despite cyber incidents.

Why is Cyber Europe 2026 relevant for companies?

The exercise shows that cyber resilience does not depend only on technical security measures. Companies must also be organisationally prepared, have clear roles, coordinate incidents and document their response.

What does Cyber Europe 2026 have to do with NIS2?

NIS2 strengthens requirements for cybersecurity, risk management, incident reporting and management responsibility. Cyber Europe 2026 shows in practical terms why these capabilities are essential in realistic crisis scenarios.

Why does business continuity management play such an important role?

Cyber incidents can interrupt critical business processes. Business continuity management helps companies maintain essential processes even during system outages, attacks or supplier disruptions.

What should companies do after Cyber Europe 2026?

Companies should review their incident response plans, BCM processes, crisis roles, supplier dependencies and evidence management. Regular tabletop exercises and realistic crisis simulations are especially valuable.

What is the main lesson from Cyber Europe 2026?

The main lesson is that cyber resilience is not created by policies alone. Companies must exercise their crisis capabilities, clarify responsibilities, understand dependencies and act in a traceable way during an incident.

3 March 2026 | 4 min

Cyber Risks in FINMA’s Focus: What Financial Institutions Must Do Strategically

Cyber risks are among the most significant operational risks in the financial sector. FINMA makes it clear that the threat landscape is not only persistently high but continues to intensify. Attacks are becoming more professional, more complex and more targeted. At the same time, digitalization, cloud adoption and outsourcing are structurally expanding the attack surface of many institutions.

Cyber risk is therefore no longer a purely IT issue. It affects governance, risk management, internal control systems and strategic decision-making processes. FINMA expects supervised institutions to adopt an integrated, risk-based and controllable approach to managing cyber threats.

  • Cyber risks are among the central operational risks in the financial market.
  • The attack surface is expanding due to connectivity, cloud solutions and third-party providers.
  • Cyber risks must be firmly embedded in governance and risk management.
  • Outsourcing and third-party dependencies are major risk drivers.
  • Institutions must report cyber incidents promptly.
  • Scenario-based exercises and recovery testing are essential.
  • Cyber resilience means protection, detection, response and recovery.

Cyber Risks as a Strategic Issue

FINMA emphasizes that cyber risks must not be treated in isolation but as an integral component of operational risk management. Technical security measures alone are not sufficient. What matters is holistic management across four dimensions:

  • Prevention
  • Detection
  • Response
  • Recovery

These elements must be organizationally embedded, documented and regularly tested.

Cyber attacks are increasingly targeted and often exploit weaknesses in outsourced services or external providers. The growing interconnection between financial institutions, IT service providers and platform operators increases systemic risk.

Governance: Responsibility at the Highest Level

A central concern of FINMA is the clear anchoring of cyber risks within governance structures. This means:

  • The board of directors and executive management are responsible for the strategic management of cyber risks.
  • Cyber risks must be part of the risk strategy.
  • Reporting to senior leadership must be structured and risk-oriented.
  • Risk tolerances must be clearly defined.

Cyber risk cannot be delegated purely as a technical matter. It is a leadership and oversight responsibility.

Outsourcing and Third-Party Risk

A significant portion of reported cyber incidents is linked to external service providers. Cloud providers, IT vendors, software providers or outsourced support functions expand the risk landscape considerably.

FINMA expects:

  • A complete inventory of all critical service providers
  • Clear classification of outsourced functions
  • Contractually defined security requirements
  • Monitoring mechanisms and control rights
  • Inclusion of third parties in emergency and crisis exercises

Without transparent management of outsourcing risks, structural vulnerabilities arise.

Detection and Response Capabilities

Many institutions operate technical monitoring systems. However, the challenge often lies in organizational coordination.

Key questions include:

  • Who makes decisions during an incident?
  • How quickly are escalation procedures triggered?
  • What communication channels are defined?
  • How are regulatory reporting obligations fulfilled?

FINMA requires clearly defined processes for identifying, analyzing and managing cyber incidents. This extends beyond IT security and involves institutional crisis management capability.

Recovery and Resilience

An often underestimated aspect is recovery capability. Cyber resilience means remaining operational even in the event of a successful attack.

This includes:

  • Tested backup strategies
  • Realistic recovery plans
  • Regular emergency exercises
  • Simulation-based testing under realistic conditions

Paper-based contingency plans are not sufficient. What matters is actual functionality under stress conditions.

Reporting Obligations and Transparency

Cyber incidents must be reported to the supervisory authority within defined timeframes. This reporting obligation is not only about regulatory transparency but also about safeguarding overall financial system stability.

Institutions therefore require clear internal processes to:

  • Properly classify incidents
  • Fulfill reporting obligations on time
  • Prepare information consistently

Lack of clarity in internal structures can lead to significant delays.

Conclusion

FINMA makes it clear: cyber risks are a strategic core issue for financial institutions. They affect not only IT departments but governance, risk management, internal controls and executive leadership.

Effective cyber risk management is characterized by:

  • Clear responsibilities
  • Integrated governance structures
  • Systematic third-party oversight
  • Strong detection and response mechanisms
  • Tested recovery processes

Cyber resilience is not a static condition but a continuous development process. Institutions that actively manage cyber risks and integrate them into their overall strategy strengthen not only regulatory compliance but also long-term stability and trust.

FAQ

What does FINMA mean by cyber risks?
Cyber risks are operational risks arising from cyber attacks, technical vulnerabilities, third-party dependencies and organizational weaknesses.

Why is cyber risk a governance issue?
Because it affects strategic decisions, risk tolerances, reporting structures and accountability at the highest level.

What role do third parties play?
External service providers significantly expand the attack surface and must be actively integrated into risk analysis, contractual arrangements and contingency planning.

What does cyber resilience mean in practice?
The ability to prevent attacks, detect them early, respond effectively and restore operations quickly.

How should institutions prepare?
By embedding cyber risks into governance structures, defining clear escalation processes, conducting regular exercises, testing recovery plans and fostering a company-wide risk culture.

22 December 2025 | 5 min

GRC Regulation 2026: New Laws and Key Dates in the DACH Region

The turn of the year traditionally marks the starting point for new regulatory requirements in the field of Governance, Risk, and Compliance. While 2025 was heavily characterized by the final implementation of major EU frameworks such as DORA and NIS 2, the year 2026 is defined by expansion and technological deepening. For companies in the DACH region (Germany, Austria, Switzerland), January 1, 2026, specifically means: Grace periods are over, new reporting standards in the crypto sector take effect, and sustainability reporting reaches the next escalation level regarding the breadth of affected companies.

  • In Switzerland, the automatic exchange of information on crypto-assets (CARF) enters into force on January 1, 2026.
  • The CSRD reporting obligation expands to large, non-capital-market-oriented companies starting with the 2026 financial year.
  • For DORA and NIS 2, the implementation phase ends; from 2026 onwards, supervisory authorities will focus on auditing and sanctioning.
  • The EU AI Act approaches decisive deadlines, making 2026 the central year for AI governance implementation.

Switzerland: Transparency Push via CARF and Expanded AEOI

A central focus at the start of 2026 lies on Switzerland. On January 1, 2026, the Federal Council enacts the Crypto-Asset Reporting Framework (CARF) as well as amendments to the Common Reporting Standard (AIA/AEOI). This is a decisive step for tax transparency in the realm of digital assets.

The CARF framework obliges Swiss crypto service providers to record transaction data of their clients and information on held crypto-assets. This data must be reported to the Federal Tax Administration (FTA), which in turn exchanges it with partner states. The goal is to close tax loopholes that existed due to the previous non-recording of crypto-assets in the classic AEOI. For GRC managers at Swiss financial institutions and crypto service providers, this means that due diligence processes and KYC procedures (Know Your Customer) must be fully adapted to the new asset classes and reporting standards by the January 2026 deadline.

In parallel, amendments to the AEOI Act come into force, implementing recommendations of the Global Forum on Transparency and Exchange of Information for Tax Purposes. This affects, among other things, more precise due diligence obligations for Non-Reporting Financial Institutions.

CSRD: The Second Wave Rolls In

At the European level, January 1, 2026, is a crucial date for the Corporate Sustainability Reporting Directive (CSRD). While previously primarily capital-market-oriented companies were subject to reporting obligations, the obligation for large limited liability companies that are not capital-market-oriented begins with the 2026 financial year.

Companies fall under this second wave if they exceed at least two of the three following criteria: more than 250 employees, more than 50 million euros in net turnover, or more than 25 million euros in balance sheet total (taking into account inflation-related threshold adjustments). For compliance departments in these companies, the start of the 2026 financial year means that data collection for the report to be published in 2027 must now be operational. The time for preparation is over; from now on, ESG data must be recorded in an audit-proof manner. This requires functioning Internal Control Systems (ICS) for sustainability information.

DORA and NIS 2: From Project Mode to Regular Operations

Both the Digital Operational Resilience Act (DORA) and the NIS 2 Directive formally entered into force before 2026. Nevertheless, January 2026 marks a watershed moment. The phase of “Day 1 Compliance,” which was often still characterized by transitional solutions, is over.

From 2026 onwards, it is expected that national supervisory authorities – such as BaFin in Germany or FMA in Austria – will intensify their auditing activities. For DORA, this means that ICT third-party risk management must not only exist on paper, but contractual adjustments with IT service providers must be concluded. Registers of information relationships must be current and complete. GRC experts should use the year 2026 to test the processes implemented in the previous year for their operational effectiveness (e.g., through TLPT – Threat Led Penetration Testing), as real sanctions now loom.

Outlook: Supply Chain Acts and CSDDD

In Germany, the Supply Chain Due Diligence Act (LkSG) remains relevant, but the focus is increasingly shifting towards harmonization with the European Corporate Sustainability Due Diligence Directive (CSDDD). Although the national implementation laws of the CSDDD will only fully enter into force later, companies must strategically align their risk analyses with the more far-reaching requirements of the EU Directive from 2026 onwards to avoid double work. In particular, the climate transition plans, which are part of the CSDDD, require a lead time that should begin in January 2026.

FAQ

Who does the new CARF law in Switzerland affect starting January 2026?

It primarily affects Crypto-Asset Service Providers (CASPs/VASPs) resident in Switzerland. They must record client data and transactions and report them to the tax authorities.

Does my company have to create a CSRD report starting in 2026?

If your company is not capital-market-oriented but meets two of the three criteria (Balance sheet > 25m EUR, Turnover > 50m EUR, > 250 employees), the duty to collect data begins for the financial year 2026. The report itself will then appear in 2027.

What changes in 2026 regarding DORA?

Regulatorily, nothing new changes, but the grace period is over. From 2026, the first in-depth audits by supervisory authorities are expected to take place, and processes must be “lived and tested.”

What role does the EU AI Act play in January 2026?

The AI Act is already in force, but many obligations for high-risk AI systems only become strictly effective in mid-2026. January 2026 is therefore the starting signal for the final implementation phase of these requirements.

11 December 2025 | 6 min

Holiday gifts for business partners in the DACH region

During the Christmas season, many companies take the opportunity to thank their business partners with small gifts. These gestures strengthen relationships, show appreciation and are often part of a company’s culture. At the same time, tax rules, compliance requirements and internal guidelines must be respected – and these differ between Germany, Austria and Switzerland.

This article provides a current and balanced overview of the legal and practical framework for holiday gifts in all three DACH countries. It explains what companies should consider in order to give appropriately, avoid risks and maintain trust.

  • In all three countries, the same core principles apply: gifts must be business related, appropriate and transparent.
  • Germany has a tax threshold of 50 euros per recipient and calendar year for business gifts.
  • Austria and Switzerland do not use a single statutory value limit, but focus on appropriateness, business purpose and documentation.
  • Clear internal guidelines and consistent documentation are recommended throughout the DACH region.
  • Gifts to people in the public sector or highly regulated industries require particular caution.

Why clear rules are important in all three countries

Regardless of whether a company is based in Austria, Switzerland or Germany, gifts must never give the impression that they are intended to influence business decisions improperly. Compliance standards, anti-corruption rules and tax legislation are designed to ensure clean business relationships.

Companies should therefore apply clear and comprehensible principles in every country in which they operate. This prevents misunderstandings, reduces legal and tax risks and creates a uniform standard for all employees.

Current regulations at a glance

Germany

Germany is the only DACH country with a clearly defined tax limit for gifts to business partners. Business gifts are tax deductible up to 50 euros per recipient and calendar year if they are business related and properly documented.

For gifts that exceed this amount, the tax deduction may be denied unless the gift is clearly and exclusively usable for business purposes.

Austria

Austria does not work with a uniform fixed value limit. Instead, the following aspects are crucial:

  • the gift must serve a clear business purpose
  • the value must be reasonable in relation to the relationship and the occasion
  • the gift must be documented in a comprehensible way

As in the other DACH countries, gifts must not be used to gain improper advantages. Particular care is required in the public sector and in strongly regulated industries.

Switzerland

Switzerland also has no statutory standard limit for gifts to business partners. The focus is on:

  • usual appropriateness according to Swiss business practice
  • transparency and traceability
  • compliance with internal rules and industry-specific regulations

Swiss business culture tends to favour modest, high-quality but unobtrusive gifts rather than expensive luxury items.

Common basic principles for the entire DACH region

Despite the legal differences, companies in Germany, Austria and Switzerland can follow a common set of basic rules.

Appropriateness

The gift should match the business relationship, the role of the recipient and the occasion. Very expensive or flashy gifts can quickly appear inappropriate.

Business purpose

Holiday gifts should always serve a legitimate business purpose, such as maintaining a good relationship or thanking partners for successful cooperation. They must not be used to steer decisions or promises of business.

Documentation

For every gift, companies should record at least the following:

  • name of the recipient and company
  • occasion
  • date
  • value
  • business purpose

This documentation helps during tax audits and internal or external compliance checks.

Caution with public sector recipients

For employees of authorities, public hospitals, universities, municipalities and similar organisations, stricter requirements usually apply in all three countries. Often only very small tokens are permitted, and in some cases gifts are completely prohibited. When in doubt, it is better to ask in advance or avoid gifts altogether.

Recommendations for companies in the DACH region

  1. Create a clear, written gifting policy that applies in all locations.
  2. Define maximum values for gifts per person and per year.
  3. Ensure consistent documentation of all gifts to business partners.
  4. Pay special attention to sensitive sectors such as the public sector, healthcare or regulated industries.
  5. Plan gifts early and avoid borderline cases in terms of value or type of gift.
  6. Consider alternatives such as charitable donations in the name of a business partner instead of material gifts.

Why restraint is often the best strategy

No matter in which of the three countries a company operates, gifts that are too expensive or too personal can send the wrong signal. They may be perceived as an attempt to influence decisions and can trigger tax or compliance issues.

Modest, tasteful gifts or a personal handwritten card are often more effective and credible than high-value items. What counts in the long term is trust and partnership – not the material value of a present.

FAQ – Frequently asked questions in the DACH region

Is there a single value limit that applies to the whole DACH region?

No. Germany has a defined tax threshold of 50 euros per recipient and calendar year for business gifts. Austria and Switzerland use the principles of appropriateness, business purpose and documentation instead of fixed legal limits.

May I give expensive gifts in Austria or Switzerland if they seem appropriate?

In principle this is possible, but it is usually not advisable. High-value gifts increase the risk of compliance concerns, negative perceptions and disputes during audits. In practice, modest gifts are safer and more in line with expectations.

How should a business gift be documented correctly?

For each gift you should record who received it, for which company the person works, the date, the occasion, the value and the business reason. This information should be stored centrally, for example in a simple gifts register.

Are gifts to employees treated in the same way as gifts to business partners?

No. Gifts to employees are subject to different tax and payroll regulations in all three countries. Companies should therefore treat gifts to staff separately from gifts to external business partners and observe the respective rules.

How should I handle gifts to governmental bodies or public organisations?

With particular caution. In all DACH countries there are strict rules for the public sector, and many organisations either prohibit gifts completely or limit them to very small amounts. If you are unsure, ask for written guidance or refrain from giving a gift.

28 November 2025 | 4 min

FINMA Risk Monitor 2025: The Key Risks for Swiss Financial Institutions

FINMA has released its Risk Monitor 2025, offering a comprehensive overview of the most critical risks facing the Swiss financial sector over the next three years. Banks, insurers, asset managers and other financial institutions must contend with a mix of traditional financial risks and newly emerging challenges linked to digitalisation, geopolitics and increasingly complex value chains.

The report makes one thing clear: institutions need stronger governance, more effective risk oversight and a more mature compliance culture to remain resilient in a rapidly evolving landscape.

  • The FINMA Risk Monitor 2025 outlines nine major risks that will be crucial for the Swiss financial industry in the coming years.
  • Particularly important are real estate and mortgage risks, credit and market risks, cyber and ICT risks, money laundering threats and outsourcing dependencies.
  • Many risks remain at elevated levels or are increasing.
  • FINMA formulates concrete supervisory expectations, especially around risk culture, technical resilience, monitoring, outsourcing controls and crisis preparedness.

Why the Risk Monitor 2025 Matters

The Swiss financial centre is highly international, strongly digitalised and significantly exposed in areas such as mortgage financing. Rising interest rates, geopolitical tensions, technological dependencies and new business models increase the pressure on institutions to identify, assess and manage risks proactively.

The Risk Monitor acts as an early warning system. It highlights where vulnerabilities are emerging, where systemic threats may arise and which areas FINMA will scrutinise more closely. For GRC functions, the report provides a clear roadmap of the areas requiring the highest priority.

The Most Important Risks at a Glance

The Risk Monitor 2025 describes several major risk categories. The most relevant include:

Real Estate and Mortgage Risks

The Swiss property market remains tight, with high prices and persistent demand. At the same time, interest rates and leverage ratios have risen, while household debt levels remain high. FINMA expects institutions to apply strict lending standards, conduct realistic stress tests and closely monitor their exposures.

Credit and Market Risks

Volatile markets, geopolitical uncertainties and higher credit spreads increase pressure on institutions. The report emphasises the need for risk-based credit management, adequate value adjustments and close monitoring of concentrated exposures.

Money Laundering and Sanctions Risks

International business models, cross-border activities and new digital financial products increase exposure to financial crime. Institutions must enhance customer risk assessments, strengthen monitoring systems and ensure consistent reporting. A strong risk culture and adequate compliance resources are essential.

Cyber and ICT Risks

With digitalisation accelerating, cyber and ICT risks continue to rise. Attacks on financial infrastructure, failures of IT providers or vulnerabilities in third-party software can have severe consequences. FINMA expects robust systems, effective incident response plans and stringent ICT governance.

Outsourcing and Third-Party Risks

Many institutions rely heavily on outsourced or cloud-based services. This reduces costs but increases vulnerability. FINMA demands clear governance over outsourcing arrangements, monitoring of service providers and the ability to maintain critical functions even during disruptions.

Liquidity and Funding Risks

Even though liquidity conditions appear stable, market stress can quickly lead to funding pressure. Institutions should monitor risk indicators, run scenario analyses and ensure they remain capable of acting in adverse conditions.

What GRC Teams Should Do Now

The Risk Monitor’s message is clear: strong governance, rigorous risk management and consistent compliance are essential for financial stability. Institutions should:

  • update their enterprise-wide risk assessments based on the FINMA risk categories
  • strengthen risk culture through clear responsibilities and open communication
  • conduct regular scenario analyses and stress tests
  • improve cyber and ICT resilience, including incident and recovery planning
  • map and monitor all outsourcing arrangements and third-party dependencies
  • enhance AML/KYC processes and reassess monitoring systems
  • define transparent reporting and escalation channels
  • modernise technological infrastructure to detect risks earlier

Conclusion

The FINMA Risk Monitor 2025 shows that the Swiss financial sector faces a demanding and highly dynamic risk environment. Many risks remain elevated and require active, forward-looking management. For GRC leaders, this means strengthening governance structures, improving risk transparency and promoting a culture in which risk awareness is embedded across the organisation.

Institutions that act early will not only meet regulatory expectations but also build long-term resilience and trust.

FAQ

What is the FINMA Risk Monitor?
An annual report identifying the most important risks to the Swiss financial market and outlining the supervisory expectations associated with them.

Which risks are highlighted in 2025?
Real estate and mortgage risks, credit and market risks, cyber and ICT risks, money laundering risks, outsourcing risks and liquidity risks.

Why are cyber risks so prominent?
Because cyberattacks and ICT failures have increased significantly in frequency and impact, and can cause rapid, widespread disruption.

What does risk culture mean?
A mindset where all employees actively identify, report and manage risks, not only the compliance or risk department.

What should institutions do now?
Reassess risks, strengthen ICT resilience, improve governance and monitoring, ensure transparent reporting and oversee outsourcing arrangements more rigorously.

16 September 2025 | 3 min

Switzerland Plans Cyber Resilience Law: A Key Step in GRC

Switzerland is responding to growing threats in cyberspace. On August 20, 2025, the Federal Council decided to draft legislation on the cyber resilience of digital products. The Federal Office for Cybersecurity (BACS), together with the Federal Office of Communications (BAKOM) and the State Secretariat for Economic Affairs (SECO), has been tasked with preparing a consultation draft by fall 2026. The goal is to establish binding security requirements for products with digital elements and strengthen market surveillance for such products.

  • The Federal Council intends to enshrine cyber resilience of digital products in law
  • BACS, BAKOM, and SECO will draft a consultation template by fall 2026
  • Security obligations for the development and marketing of digital products will be defined, including import and sales bans on unsafe devices
  • Market surveillance will be enhanced to ensure vulnerabilities are identified and addressed quickly
  • Switzerland is aligning itself with EU regulations such as the Cyber Resilience Act and the NIS-2 Directive

Why This Matters

Digital products have become part of every aspect of life – from smart devices to IoT, software, and connected hardware. If vulnerabilities exist in such products, the consequences can be severe for users, businesses, and critical infrastructure. To date, Switzerland has had very few binding regulations on cyber resilience of digital products. With the new initiative, this regulatory gap will finally be closed.

What Will the New Legislation Cover?

The law is expected to include:

  • Security requirements for the development and marketing of digital products
  • Market surveillance rules to prevent unsafe products from being sold or imported
  • Minimum standards for updates, patches, security testing, and disclosure of vulnerabilities
  • Enforcement mechanisms and sanctions for non-compliance

Comparison to EU Initiatives

InitiativeFocusScopeLink to Switzerland
Cyber Resilience Act (CRA)Security requirements for products with digital elements, lifecycle, updates, reporting obligationsMandatory across the EU from 2027Switzerland aims to adopt similar standards
NIS-2 DirectiveProtection of critical infrastructure and services against cyberattacks; reporting and preparedness obligationsApplicable in all EU member statesSwitzerland aligns its framework with EU norms
EU Cybersecurity Act, CER, DORABroader regulations on cybersecurity, resilience, and financial servicesEU-wide frameworksServe as benchmarks for Switzerland

Benefits and Challenges for Switzerland

Potential Benefits

  • Stronger protection for consumers and businesses
  • Increased trust in digital products and providers
  • Legal certainty for manufacturers and importers
  • Reduced costs from security incidents through preventive measures

Challenges

  • Overly strict requirements may hinder innovation
  • Smaller manufacturers may struggle with compliance costs
  • Effective enforcement and market surveillance require significant resources
  • Harmonization with international supply chains is essential

Conclusion

The planned Swiss cyber resilience law marks an important step toward modern cybersecurity policy. It closes an existing regulatory gap, establishes binding requirements for digital products, and aligns with proven EU initiatives. For companies, now is the time to proactively integrate compliance, governance, and risk processes to avoid costly adjustments later.


FAQ

What is cyber resilience of digital products?
It refers to the ability of hardware and software with digital elements to remain secure, resist attacks, and quickly fix vulnerabilities.

Why is Switzerland introducing this law?
Because there are currently no binding national rules, despite rising risks from insecure digital products.

When will the draft be ready?
A consultation draft is expected by fall 2026.

What requirements are likely to apply?
Security by design, mandatory updates, vulnerability disclosure, and bans on unsafe devices.

How does this compare to EU laws?
Many elements mirror the Cyber Resilience Act and NIS-2 Directive, which also focus on minimum requirements, reporting duties, and market supervision.

What should companies do now?
Review product portfolios, implement security processes, adjust governance structures, and align with EU standards early.

25 March 2025 | 3 min

The Mozambique Affair of Credit Suisse: A Cautionary Tale of Compliance Failure and the Need for Robust GRC

What is the Mozambique Affair?

The so-called Mozambique Affair involving Credit Suisse is one of the most serious financial scandals in recent years. At its core are hidden loans worth billions of dollars, dubious offshore transactions, and extensive allegations of corruption. This scandal vividly demonstrates how inadequate compliance and governance structures can not only bring banks to their knees but also cause devastating economic and political consequences for an entire country.

The Scandal in Detail: Hidden Loans and Opaque Financing

Between 2013 and 2016, Credit Suisse, together with other financial institutions, arranged loans amounting to approximately USD 2 billion for Mozambique. These funds were officially intended for maritime security projects and the development of the tuna fishing industry. However, large portions of the funds were misappropriated or vanished into opaque channels.

The critical issue: The loans were not recorded in Mozambique’s state budget and were therefore kept secret. Key institutions such as the parliament, the International Monetary Fund (IMF), and donor countries were deliberately kept in the dark. When these “hidden debts” became public, confidence in Mozambique’s government collapsed, plunging the country into a severe debt crisis.

Compliance Failures on Multiple Levels

The Mozambique Affair highlights significant weaknesses in Credit Suisse’s compliance structures. Key compliance failures included:

  • Inadequate due diligence: The vetting of loan recipients and verification of loan utilization were insufficient. Politically exposed persons (PEPs) were involved without adequate risk assessments.
  • Poor risk management: Despite obvious red flags, the loans were approved. Internal warning signals were ignored or not systematically pursued.
  • Failure of internal control systems: Mechanisms designed to scrutinize transactions for legality and transparency either failed or were bypassed.
  • Conflicts of interest and lack of independence: Compliance departments lacked sufficient independence from commercial divisions, contributing to a culture of turning a blind eye.

Consequences for Credit Suisse

Credit Suisse faced fines from multiple regulatory bodies and had to settle for millions in penalties. The bank’s reputation suffered significantly. The scandal was a key factor in the erosion of trust in the bank’s leadership and contributed to its eventual acquisition by UBS.

How Effective GRC Can Prevent Such Scandals

Governance, Risk & Compliance (GRC) is not a bureaucratic formality—it is a core component of modern corporate management. An effective GRC framework could have prevented many of the issues exposed by the Mozambique Affair. Key success factors include:

  • Strong governance structures: A clearly defined control environment with transparent responsibilities helps prevent abuse of power and lack of transparency.
  • Risk-based compliance programs: Integrating risk assessments into decision-making ensures that transactions with high reputational or financial risks are identified early.
  • Independent and empowered compliance functions: Compliance teams must operate independently and have direct access to senior management.
  • Transparent reporting and communication channels: Internal and external stakeholders must be informed about critical business activities. Whistleblower systems should be protected and actively encouraged.
  • Ongoing training and awareness programs: Employees must receive regular training on ethics, integrity, and regulatory requirements.

Conclusion: Lessons from the Mozambique Affair

The Mozambique Affair is a stark reminder of the devastating effects of weak compliance and poor governance. It underscores the importance of viewing GRC not as a checkbox exercise but as a strategic success factor. Only with robust structures, transparent processes, and a true culture of integrity can such scandals be prevented in the future.

A functioning GRC framework not only protects against regulatory penalties—it protects the organization from itself.